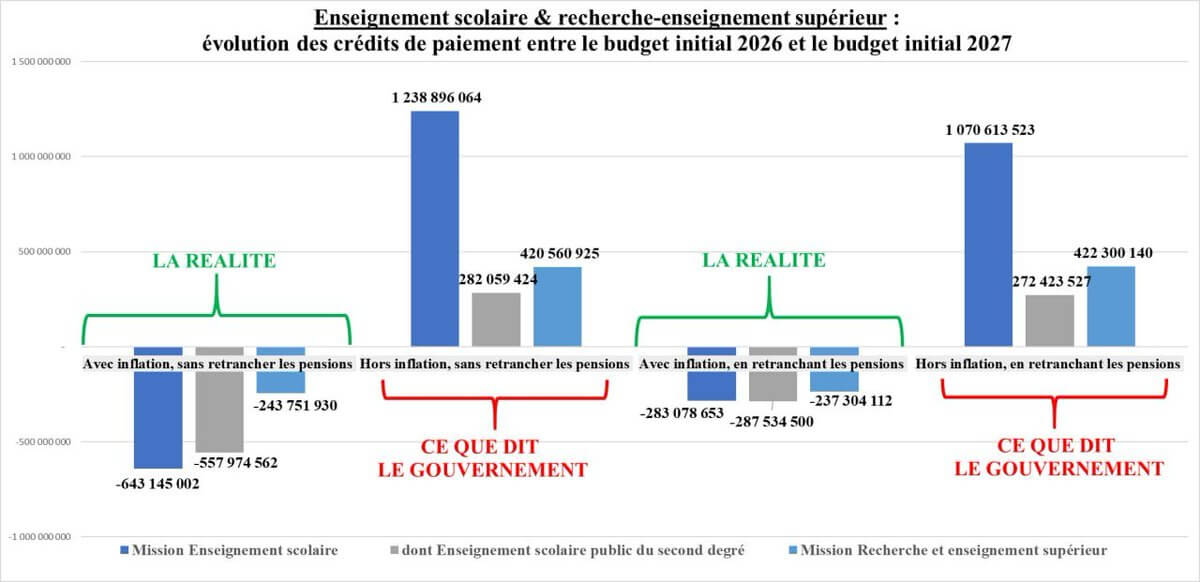
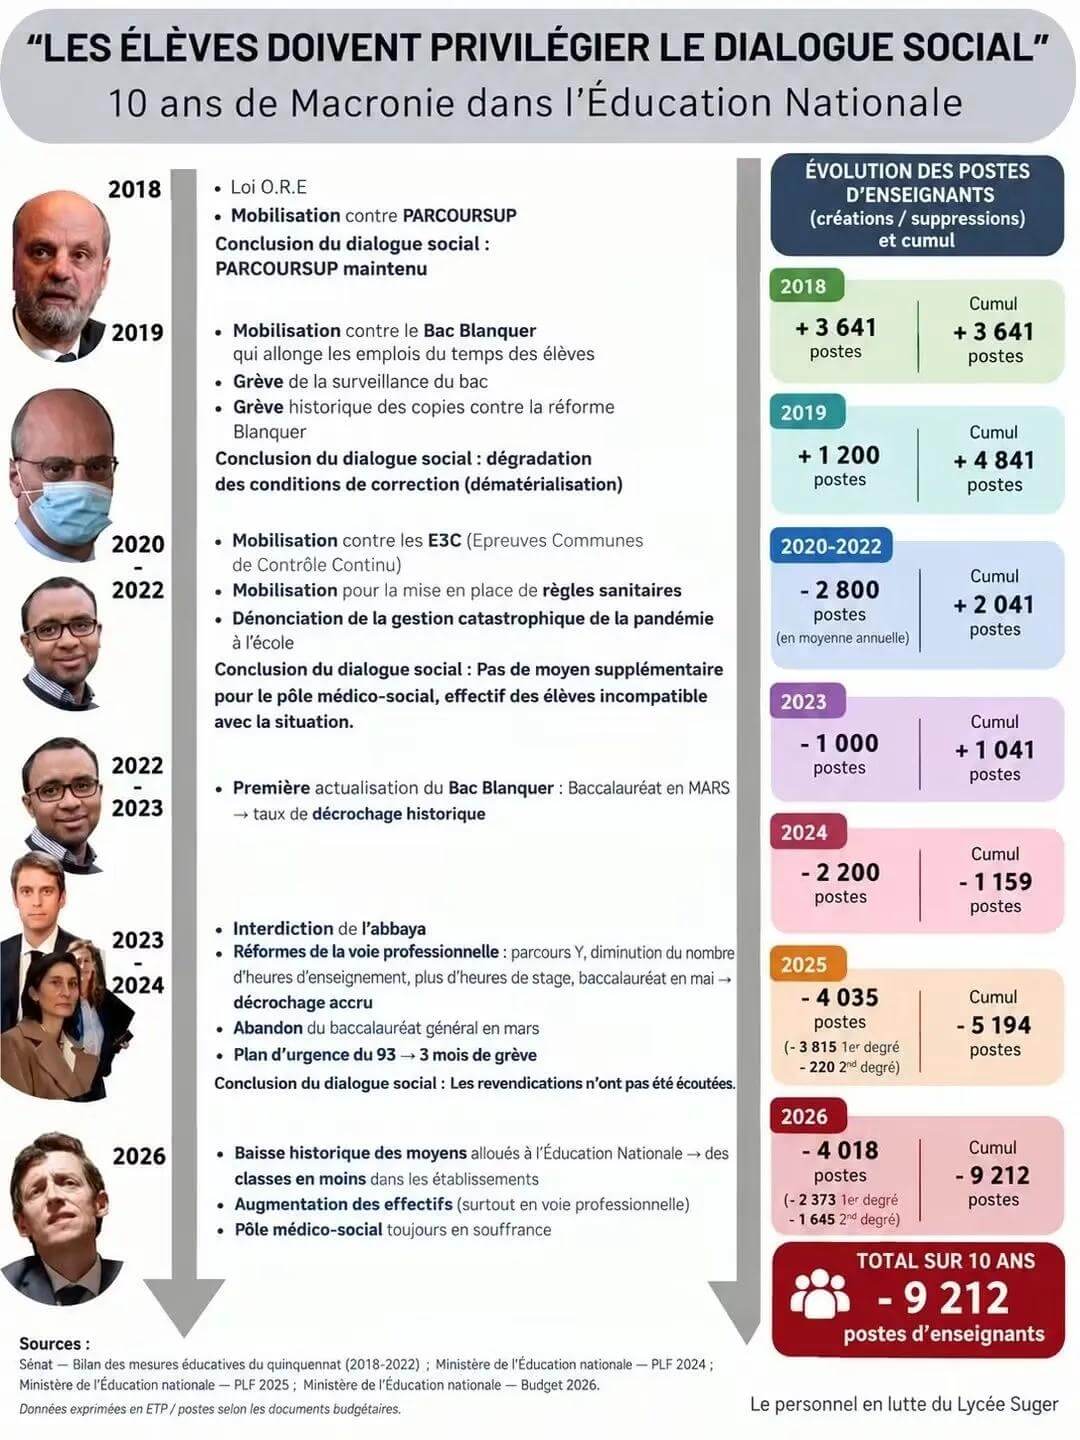
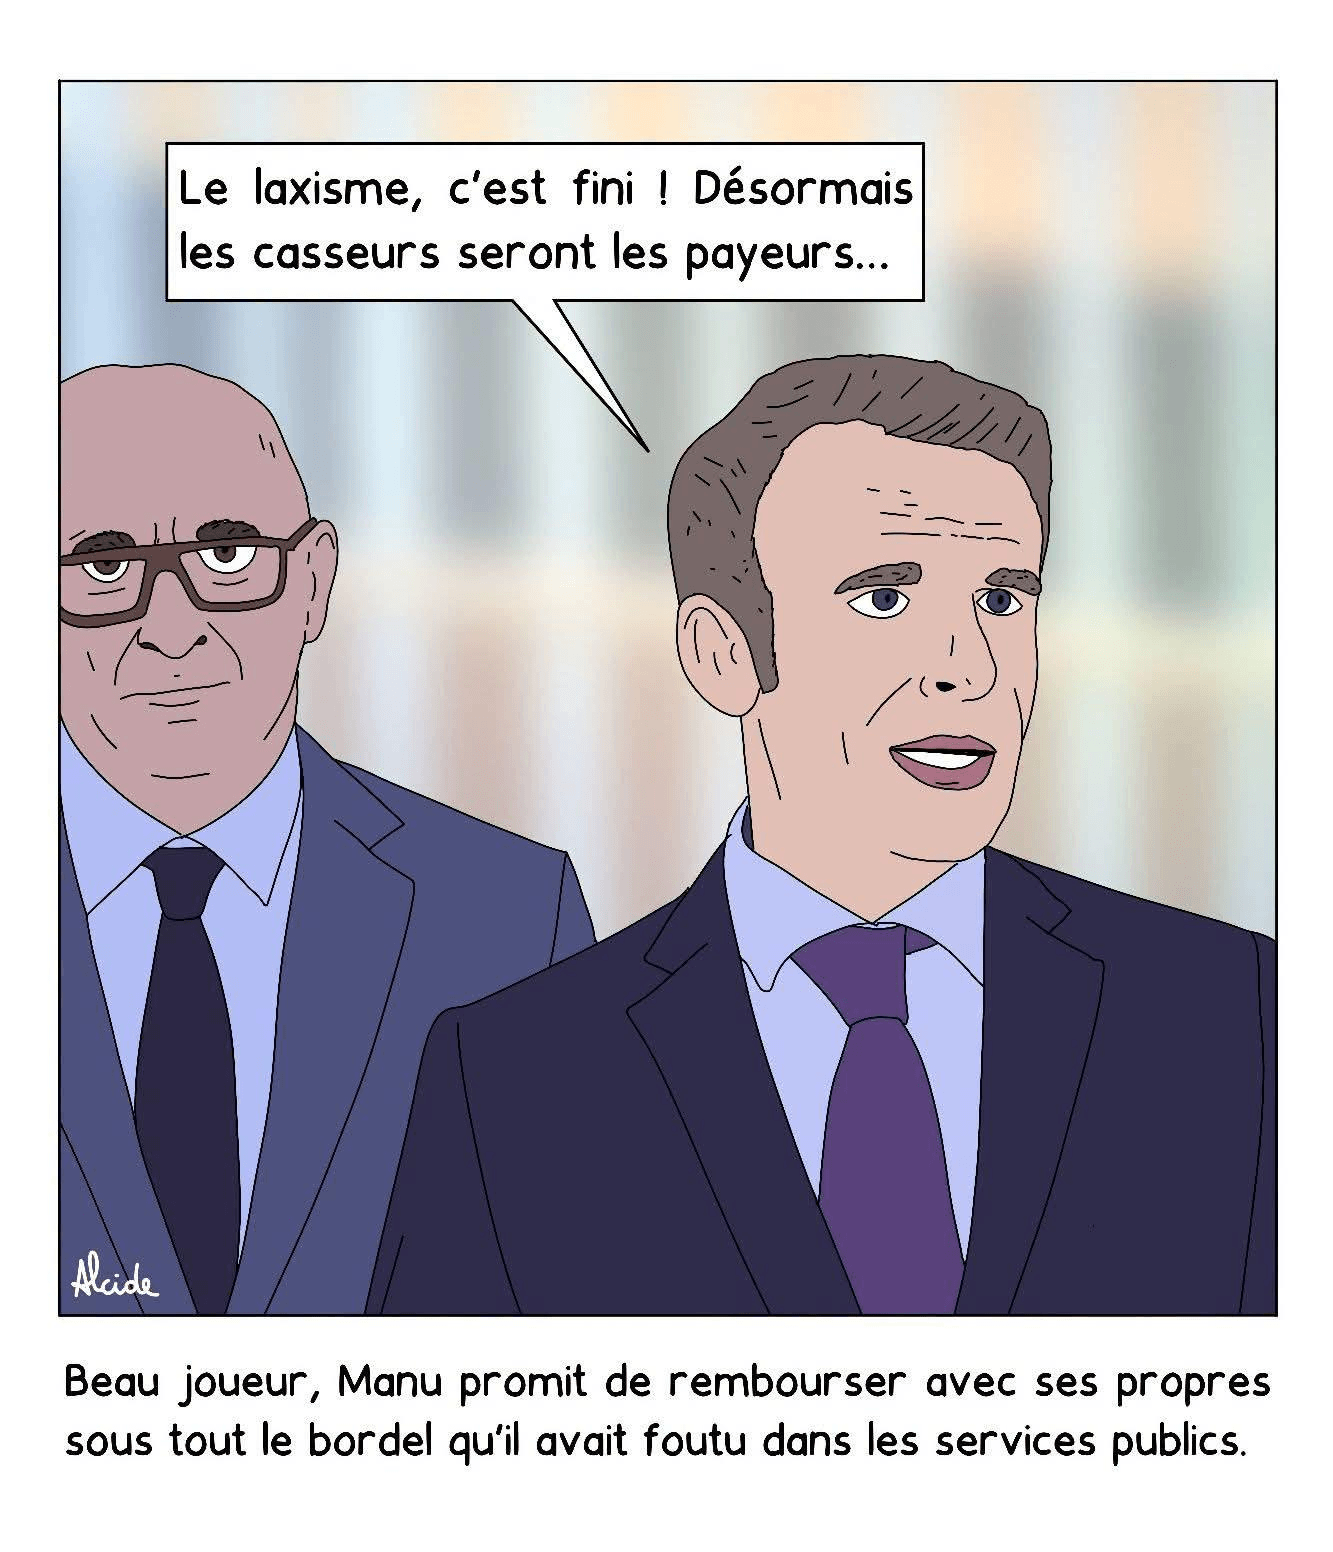
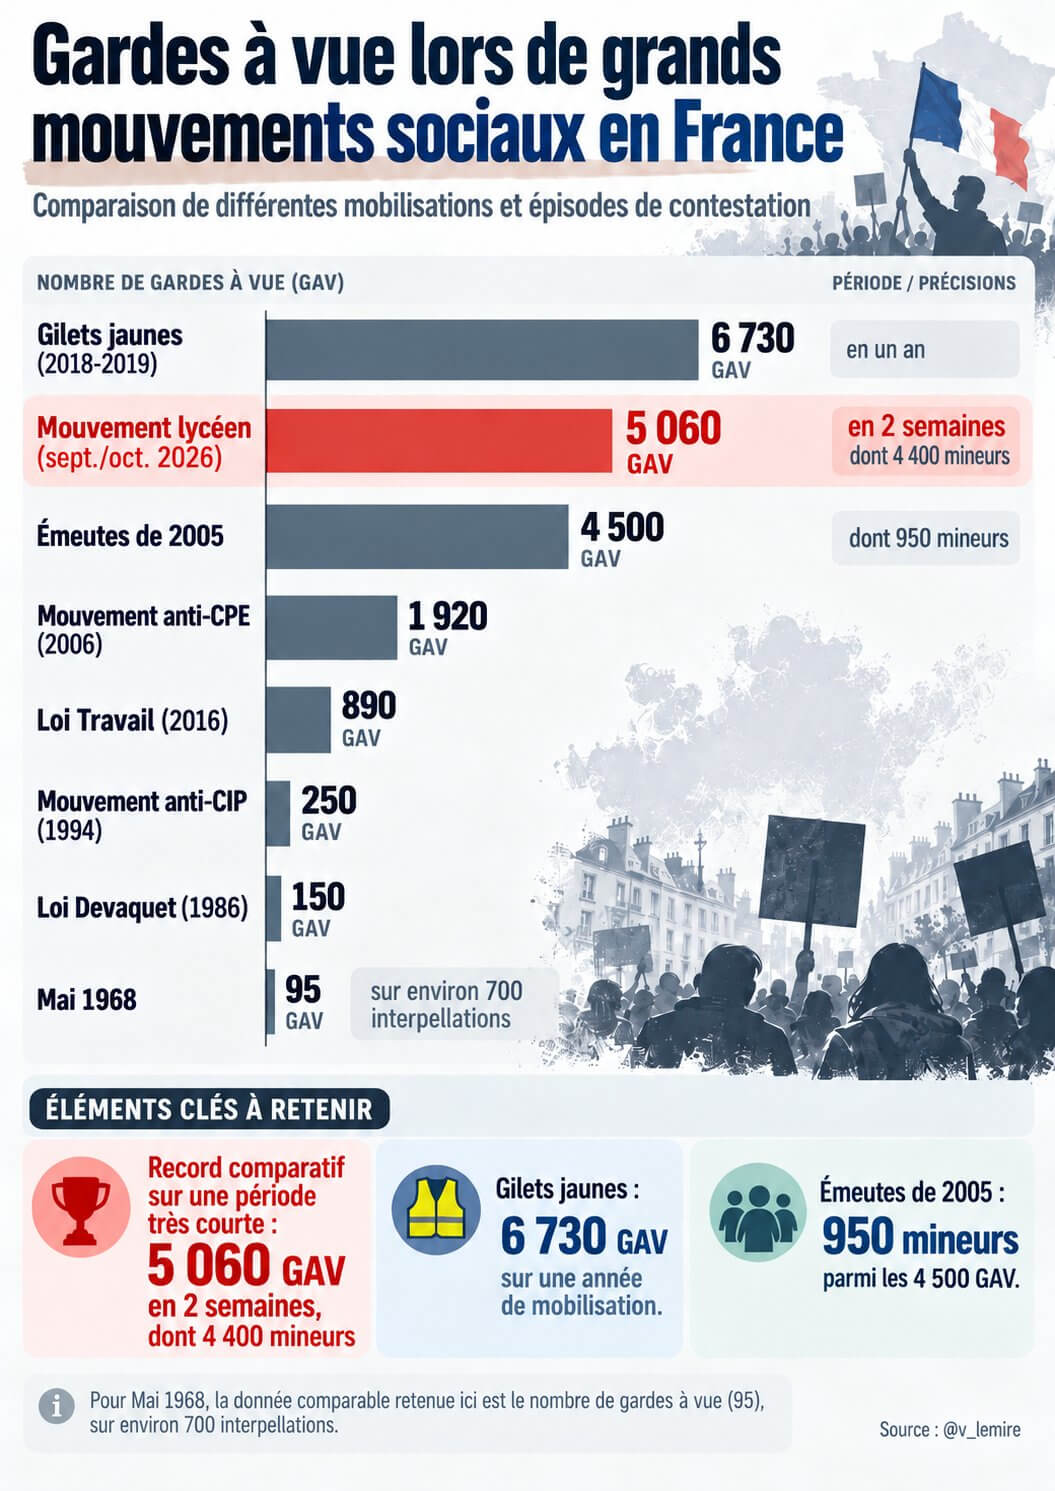
❌

Modalità di lettura

⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More

Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about it. But speed is only part of the problem. A secure connection didn't always mean a safe destination. People offering to fix a ransomware mess had questions to answer themselves.

  •  

Microsoft blames a configuration change for Exchange Admin Center tumble

Microsoft took down the Exchange Admin Center (EAC) today after a code change left administrators facing an "Internal Server Error" when trying to access the service. Microsoft first admitted that something was amiss at 0937 UTC on October 12, noting, "When attempting to access the Exchange admin center, affected admins may encounter an 'Internal Server Error' message." Any administrator attempting to access the EAC could be affected. It was more than an hour before the company stated: "We've identified unexpected 302 redirect errors during affected Exchange admin center (EAC) access attempts and are analyzing diagnostic logs to isolate the source of the access failures. "While we continue our investigation, admins remain unable to access the EAC, with no workaround currently available." So, a fun morning for Microsoft's European users. According to Microsoft, the EAC is "a modern, web-based management console for managing Exchange Online." Want to manage mailboxes? EAC is where you go. Group management? Again, EAC. Microsoft explained: "The design of the EAC in Exchange Online aligns with the overall Microsoft 365 admin experience." Sadly, that alignment appears to extend to service wobbles caused by changes rolled out without due care and attention. Two hours after admitting things had gone awry, Microsoft said it was "continuing to test the rollback of the recent Exchange admin center (EAC) change while monitoring the results to determine if this resolves the impact." At this point, administrators were nodding sagely at an all-too familiar story. Of course rolling back the change did the trick. Microsoft stated as much in its final update: "A recent EAC configuration change resulted in unexpected HTTP responses within the affected request path, preventing admins from successfully accessing the EAC. "Reverting the identified change restored expected service functionality." Microsoft also assured customers it was reviewing the change to ensure it didn't make the same mistake again, as well as its monitoring and telemetry, to "improve detection and alerting for similar service behavior." The problem is that this is hardly a new phenomenon. In September, Microsoft made a configuration change that left some users unable to access SharePoint Online sites and pages. In April, another ill-thought-through change took down Outlook for iOS. And, in 2025, Microsoft 365 tumbled from the cloud because of yet another configuration change. It's almost as if testing changes consists of little more than asking Copilot, "does this look alright to you?" and then hitting the go button. The latest outage was resolved before the end of the working day, and a preliminary Post-Incident Report is due within two business days, with a final report due next week. Hopefully one or the other will contain words along the lines of "Hey, this keeps happening, maybe we should do some more testing before deploying to production?" ®

  •  

Chatbot refuseniks edge out users in the US, and they’re not for turning

If you thought everyone was into chatbots, think again: about half of US adults never use the AI tools, and most have no interest in starting. According to Pew Research Center, older adults are the least likely to use chatbots, with roughly three-quarters of those aged 65 and older saying they never use them. That may be expected, yet more than half (58 percent) of adults aged 50 to 64 don't use them either. Those aged 18 to 29 use chatbots the most, at 66 percent, however even a third of them say they never do. About four in ten under 50 report not using them at all. Across all adults, 51 percent are chatbot refuseniks, so users are - just barely - the minority. Pew asked non-users to choose from five possible reasons. Six in ten cited simple lack of interest as a major factor, followed by the more familiar concerns of data privacy and the accuracy of chatbot answers. Some Reg readers might suspect older people avoid chatbots because they lack tech-savviness, but fewer than a third cited not knowing how to use them as a major reason. The authors of the survey also found fewer than one in five worried about what others might think of them for using the technology, so social stigma isn’t the deterrent either. Adoption also differs by race and ethnicity: non-users are more likely to be white, black or hispanic than Asian, according to Pew’s survey. The AI dodgers don't look ready to budge. Two-thirds (67 percent) say they’re unlikely to use the technology in the next 12 months, including 40 percent who say they’re not at all likely to change their mind. Another 12 percent are unsure, and just 5 percent of non-users think they'll probably try a chatbot over the next year. Perhaps abstainers were put off by a bad experience, such as Microsoft’s notorious racist chatbot Tay a decade ago. Or something more recent, like the Trump administration’s official America.gov service, which at the time of writing still displays a hotdog if you type that into the prompt. ®

  •  

No shame in the Domain Name game: DNS is doomed, literally

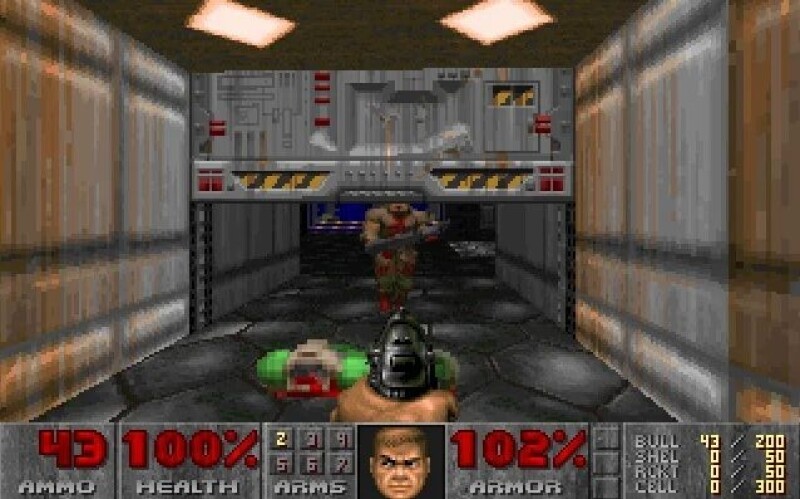
What is DNS? That's right, it's a database. You can disagree with me but you would be wrong. What can you put in a database? Strings, ints (and you learn the difference right quick if your AWS account ID has a leading zero!), JSON objects, coordinates; some of the databases out there have some pretty esoteric types. PostgreSQL supports circle, a polygon, a macaddr8, and a tsquery. Oracle will store a ROWID and your dignity. In a word, databases store data. Can you put answers in a database? Well sure; you could record that "3 + 2 is equal to 5" and store that answer. You can do the same with comparison operators; "3 is larger than 2" and so on. Take it a step further and you've built something with your database: a remarkably inconvenient calculator. So now we've established that you can store arithmetic and decisions in a database. And what can we do with those things? That's right, we can follow instructions! Good job! And what does following instructions require? Generally, memory; a place to store your numbers, your instructions, and which instruction comes next. If only we had a place to store those things. Oh right, we do; we have a database! Now connect those lookups together. Read an instruction, look up an answer, save the result, repeat as needed. So what have we built? That's right: a computer! And what can a computer run? Programs! My, you're quite good at this. And now, gentle reader: what program do we apparently have a moral obligation to run on every computer? Oh yes, though many of you are going to sit back and instead say "oh no" as the horror courses through you. I am talking about Doom. This very publication agrees with me! What have I done? That's right; I have compiled Doom for a 32-bit machine whose arithmetic and memory live in DNS. A small program supplies the wiring and the clock, neither of which the architects of DNS saw fit to include. But DNS does supply the answers. So, can we play Doom? Only if it's turn-based. It won't render on human timescales anyway. In my first attempt, I pressed Right, and then waited for 577 seconds to find out what happened. By using native transport, pipelining, packing registers densely, and optimizing instruction blocks, I was able to drop that to 146 seconds, before I hit a wall. BIND answers in about 7 µs per query over TCP and 4 µs over UDP, which is fast. The problem is that a 32-bit add is four DNS lookups, a branch is five, and a frame needs 6.6 million of them, so don't use a server that charges per request. And what do we do when BIND isn't performing the way we want it to? I don't know what you do, but I publish my code, then reach out to Paul Vixie, DNS pioneer and architect of BIND 8 to unjustifiably complain. Paul then apparently congratulates me on "the best use of RFC 2136 DNS UPDATE" that he'd ever seen. Given that he's a co-author of that RFC, I suspect he's seen a lot! Which was gratifying, but unhelpful. So let's take another crack at it. What if I do lookaheads? Good thought, bad outcome, because BIND is bound by message count, not chain depth. Well okay, I have some more tricks in my Big Bag of Stupid Ideas. So I went a bit further and via committing registers to DNS less often, moving lookups to UDP, telling BIND to stop padding answers with authority records, and requiring fewer lookups per instruction, I was ultimately able to get that press-right time down from 577 seconds to 146.3 seconds to 54.4 seconds, for a 10.6x improvement. And now I think I have hit a wall. Even at one DNS exchange per instruction (which is far better than anything realistically achievable), 1.4 million instructions at roughly 10 µs each is 14 seconds per tick. Doom says its tic rate is 35 per second, so "playable" is a tic every 28.6 ms. I remain at 54,000 ms, which is three orders of magnitude away from victory. Okay seriously, WHAT? This legitimately works. Every commit is an RFC 2136 UPDATE with a hard requirement: it fails unless the previous state is still exactly what was last written. Apparently "real" database people call that optimistic concurrency, or compare-and-swap. Joke's on you, friends; DNS has shipped with that since 1997; has your inferior database? The database itself is 6.4 million rows of truth tables. ff.01.0.add holds "001": 255 plus 1 is 00 carry 1. DNS is just acting as a librarian here, fetching memorized answers to any arithmetic question in-scope and returning the answer upon request. It's also verifiable! The frame that's spat out is checked on every pixel against an independent emulator. If one record is corrupted in the AND table, the answer changes, which proves there's no local fallback doing arithmetic for us. I've included tooling so that reviewers can run two commands against that repo and verify correctness. I also confess I cheated slightly here; the run I'm pulling these numbers from started from a checkpoint prepared by a normal emulator. It turns out that for SOME UNKNOWN REASON getting a cold boot through Doom's startup screens via DNS would take hours. Also, before the timer starts, DNS has to load those 6.4 million records, so it's a computer that takes roughly a minute to boot before it can even start. We can't cheat This runs atop nothing special: Debian's stock BIND 9.20, configured through named.conf. It lives in a container with networking disabled. I want to be very clear here: this isn't DNS pretending to be a CPU. The instruction decoding is done ahead of time by a compiler; BIND never executes an instruction itself. All that it sees is a key-value read, a conditional write, and 6.4 million rows of precomputed answers. So instead, think of this monstrosity as a database with a key-value read, a conditional write, and 6.4 million rows of precomputed answers. It's not really a computer; it's simply a very good database. And that turns out to be enough. ®

  •  

Leading digital change when nobody prepared you for it

By Louise John, Head of IT Service Delivery at Virgin Active

For IT managers, unexpected projects and changing business priorities are normal part of the job.

You might have spent months planning your team’s workload, but only to be told with little warning that a new software solution needs to be implemented within six weeks.

Whatever the circumstances, the responsibility for delivering these projects often falls on IT teams, even when they have had little involvement in the decisions behind them.

As a manager, this can be particularly challenging because you are expected to deliver results within tight deadlines, while also managing your team’s existing workload, keeping up staff morale while also protecting them from burnout.

So, how can you support your team when unexpected projects land on their desks?

Prioritise and manage expectations

The first thing I would recommend is establishing what actually needs to be delivered and by when.

If a new software implementation has been given a six-week deadline, what are the absolute essentials that need to be completed within that timeframe?

Rather than attempting to deliver everything at once, identify what is achievable and communicate this to senior leadership. Managing expectations upwards is just as important as managing the team responsible for delivery.

It’s also important to involve your team in these conversations. Be honest about what is expected, explain the priorities and ask what they realistically believe can be achieved.

Protect your team’s wellbeing

Unexpected projects inevitably create pressure, particularly when teams are already managing demanding workloads.

As a manager, you need to recognise this and consider what additional support might be required.

Could working hours be more flexible? Can existing projects be paused or reassigned? Do you need additional resources? If employees are required to work extra hours, can they take time back once the project is completed?

It’s also important to establish boundaries and make sure your team isn’t expected to deliver everything simultaneously.

When workloads become overwhelming, it helps to focus on one task at a time rather than worrying about the hundred things still to do.

Finally, don’t underestimate the importance of keeping morale high. Even during the busiest periods, celebrating small wins, recognising people’s efforts and maintaining a sense of humour can make a big difference.

Ultimately, IT managers cannot always control the projects or deadlines handed to them, but they can control how they support their teams through them.

Louise is speaking at DTX + UCX London 2026, taking place at ExCeL London on 14 and 15 October.

Join Louise on Wednesday 14 October, from 12:10pm to 12:50pm, on the Design & Delivery Stage, for a panel discussion titled Caught in the middle: Leading digital change when nobody prepared you for it.

She will be joined by Rebecca d’Orazi Flavoni, Digital Growth and Training Consultant at RDF Training & Consulting; Greg Ferrari, Executive Director of Performance and Transformation at AAT; and Roger Kirby, Senior Enterprise Architect at AstraZeneca.

Together, they will explore how managers can balance pressure from senior leadership, protect their teams from burnout and successfully deliver digital change, even when they haven’t been given the tools or context to do so.

The post Leading digital change when nobody prepared you for it appeared first on IT Security Guru.

  •  

DTX + UCX 2026: Ingram Micro on Unlocking AI and Cloud Without Losing Control

Ahead of their participation at DTX + UCX London 2026, Lee Robson, AWS Greenfield Practice Lead at Ingram Micro shares what the company will be showcasing at the event and explains what trends will impact the channel in the year ahead.

  1. How is Ingram Micro participating in DTX + UCX 2026?

Ingram Micro will be showcasing how organisations can accelerate innovation with AWS. Our team will be demonstrating practical AI, cloud and security solutions, including AWS Quick, Claude via Amazon Bedrock, FinOps-led cloud optimisation and AWS security assessments. We’ll be connecting customers with specialist partners that can help turn strategy into measurable business outcomes. 

  1. What are the key messages you will be promoting to delegates of the show?

Our message is simple: unlock the value of AI and cloud while maintaining control of cost, security and governance. We’ll be highlighting how AWS enables organisations to innovate faster, connect apps, data, and teams so answers turn into action instantly with AWS Quick, adopt generative AI through Claude via Bedrock, optimise cloud spend through FinOps, and strengthen their security posture.

  1. What are the biggest challenges organisations face when purchasing technology through the channel?

Many organisations are overwhelmed by the pace of technology change, particularly around AI and cloud. Common challenges include understanding where to start, selecting the right solutions, managing cloud costs, ensuring security and compliance, and finding the skills required to implement and support new technologies successfully.

  1. How can dedicated, experienced partners solve these challenges?

Experienced partners help customers move from technology discussions to business outcomes. With Ingram Micro, they remove the barrier to entry for a lot of businesses and provide strategic guidance, technical expertise and proven delivery frameworks that reduce risk and accelerate adoption. Partners can also help organisations optimise AWS investments, implement AI responsibly, improve security and create clear roadmaps for long-term success.

  1. What trends do you believe will impact the channel in the year ahead?

Generative AI adoption will continue to accelerate, but organisations will increasingly focus on governance, security and achieving measurable ROI. We also expect greater emphasis on FinOps as cloud estates mature, alongside growing demand for cybersecurity services. Partners that combine AI expertise, cloud optimisation and security capabilities will be best positioned for growth.

The post DTX + UCX 2026: Ingram Micro on Unlocking AI and Cloud Without Losing Control appeared first on IT Security Guru.

  •  

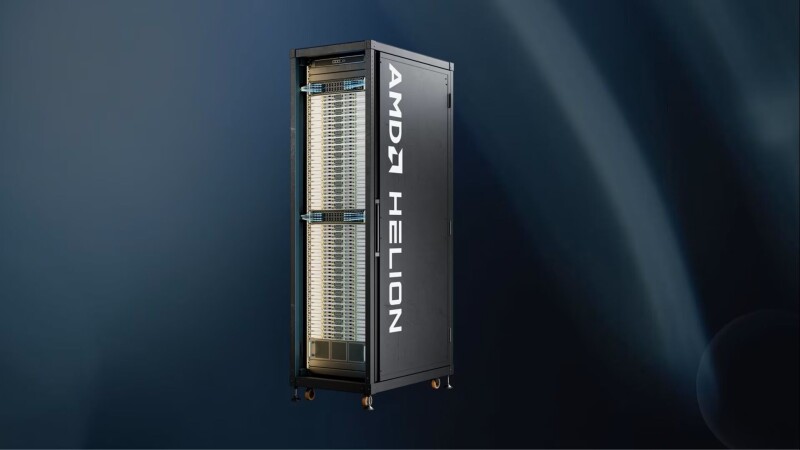
AMD unveils Helion racks for AI agents at OCP summit

AMD is expanding its rack-scale AI lineup with a design to run AI agents, offering CPU-only configurations or integrated CPU/GPU deployments, and liquid-cooled or air-cooled versions. Revealed at the Open Compute Project (OCP) Summit 2026 in San Jose, California, the chipmaker's new rack reference design is named Helion, while its existing system carries the moniker Helios, which we can't help feeling is inviting confusion a little. Helion offers an OCP-compliant blueprint for agentic AI infrastructure built around AMD's CPUs and accelerators. AMD launched Helios earlier this year for frontier-scale AI training and large-scale inference. Helion's enterprise configuration instead combines agent execution and inference within a single rack. Customers can opt for a CPU-only hyperscale configuration or an enterprise configuration with a mix of CPU and GPU blades. Depending on configuration, AMD advertises up to 32,768 of AMD's "Zen 6" CPU cores, delivered via compute nodes fitted with 256-core versions of its Venice Epyc processor, up to 16 of its Instinct MI350P GPU accelerators, and up to 102 Tbps of networking bandwidth. The CPU-only hyperscale version offers dedicated capacity for agent execution and connections to separate model inference infrastructure, while the enterprise configuration combines agent execution, GPU inference, and supporting workloads in one rack. Both configurations offer dense, balanced, or high-performance CPU blades. For dense deployments, EPYC 9006 chips rated at 400 W are used, while performance blades sport a version of the chip with just 96 cores but clocked at 5 GHz. Balanced blades use 256-core processors rated at 600 W. There are also GPU inference blades, with eight Instinct MI350P GPUs in a 5U server, plus general-purpose blades, intended for database and storage servers or technical compute workloads. AMD SVP for Compute and Enterprise AI Dan McNamara said agentic AI is not a single workload, spanning enterprise applications and complex workflows, each with different compute requirements. "To do that takes optimized compute and infrastructure that can adapt to different workloads. With AMD Helion, we are bringing Epyc performance, open software and flexible rack designs together so our partners can build systems around customer needs and make efficient use of available power," he added. AMD says it plans to contribute the Helion specifications to OCP, making them available to the community for further development and adoption. Partner-built Helion configurations are scheduled for November 2026. In its announcement, AMD cites Cisco, Dell, HPE, Foxconn, Lenovo, Supermicro, and others as on board with the new kit. ®

  •  

Risolte vulnerabilità in prodotti Check Point

Check Point ha rilasciato aggiornamenti di sicurezza che risolvono 2 vulnerabilità con gravità "critica" che interessano Security Gateway, Security Management e Spark Firewall, soluzioni dedicate alla protezione del perimetro di rete e alla gestione centralizzata della sicurezza. Le vulnerabilità potrebbero consentire ad un attaccante remoto non autenticato di eseguire codice arbitrario sui sistemi compromessi
  •  

Which AI infrastructure option actually holds a boundary?

EVENT: Every sovereign AI architecture is a trade, and the currency changes with the option: capital, capability, elasticity, or the fine print about who operates it. The cost you notice last is usually the one that decides whether the pilot ever becomes production. Nobody chooses badly on purpose. They choose with the information available at the planning stage, and the costs that matter most, in capability and in operations, tend to show up later. Which is why the honest comparison is hard to get. The people who have run each option for a year are the ones who know, and they are not saying it on a recorded webinar. They will say it at dinner. On Thursday 29 October, just over two weeks from now, The Register is hosting HPE and NVIDIA in Washington with editor-in-chief Matt Rosoff in the chair and the Chatham House Rule in force. HPE sends Bharath Ramesh, Head of Product, AI Factory Solutions, and Tracy Mills, Acting Director Federal Systems Integrators & Distinguished Chief Technologist Federal. NVIDIA sends Bert Condensa, Vice President for Enterprise AI Factory Segment Sales. All three are there to take questions. The agenda is the trade-offs themselves: which infrastructure options hold a boundary, what each one costs in capital, capability or elasticity, and whether the answer survives the move from planning into operations. And the questions underneath: what can leave a jurisdiction versus what can leave the building, and what an auditor will accept as evidence a year from now. This is written for the person who owns that decision and is making it this quarter, not next year: technology, data and risk leaders in healthcare, financial services, research, pharmaceuticals, government and higher education. It is one table with no slides, everyone at it a peer, and a chair who closes down a pitch as soon as it starts. Places are filling. Dinner runs from 6.00pm to 8.30pm at Fiola Mare, Washington DC. Request one here. Government and public sector guests: where your agency’s ethics rules require it, you can pay your own share and we will provide a receipt. Please say so when you request an invitation.

  •  

Windows 11's easiest account bypass gets the Microsoft boot

Microsoft has closed a loophole that let users sidestep the need for an account during setup for consumer versions of Windows 11. If users clicked "Learn More" when the setup process prompted for a Microsoft account, the Out-of-Box Experience (OOBE) skipped directly to the point where they just had to enter a name and password. Windows prodder "Bob Pony," who first documented the loophole, reported its removal. We tried the original trick on real Intel hardware and found it was possible to skip the Microsoft account requirement by clicking a link, but no longer. Other hacks – for those who dare to use unofficial Windows setup routes – still exist, though they are beyond the skill set of the average user. Microsoft requires an account during initial setup of Windows 11 Home and Pro for personal use. For consumers, using Windows 11 without an account can be tricky because services such as OneDrive require authentication. Microsoft is far from the only operating system vendor to demand an account during setup, but many Linux distributions, by contrast, don't require one. According to Bob Pony, the loophole was "quietly patched server side," which makes sense. Microsoft was hardly likely to leave it flapping open for long. Microsoft has won this round of account workaround Whac-a-Mole, though another bypass may yet pop up. ®

  •  

Ukrainian drone strikes on Yandex datacenters knock cloud and payments offline

Yandex engineers are working to restore services after Ukraine launched drone strikes on three of its five Russian datacenters. The strikes began overnight on October 7-8, "seriously damaging" Yandex's Sasovo datacenter and leading to a total shutdown. Ukrainian drones struck again on the morning of October 9, targeting the company's Kaluga datacenter, resulting in part of its infrastructure being taken offline. Dima Pirogov, head of Yandex's fintech division, confirmed via Telegram on Sunday morning that a third strike targeted the company's Vladimir site, which supports Yandex Pay. A day later, services remain offline, although Pirogov said users' money is safe. "I'm very sorry I can't tell you yet that everything is working again," the exec wrote. "The team continues to restore services and is checking every step. When it comes to your money, it's important to us not just to restore Yandex Pay as quickly as possible, but also to ensure that everything is working reliably. "I understand that you're not waiting for words, but for access to your money. And I understand how hard it is to wait when you can't use it. We can't give you a precise timeline for the restoration yet, but we promise: we won't stop until the service is back online." Yandex Pay is the company's digital payments service. Users can make online and in-store purchases, pay in installments, and split bills with friends and family. It's also integrated into online shopping experiences. It is comparable to Apple Pay or Google Pay, while Yandex more broadly offers services similar to Google's. Yandex said engineers are prioritizing the most-used services, and reported that access to the Alice AI assistant, Mail, Maps, Search, and Taxi is being restored, but other features remain offline. The company's status page lists widespread outages across Yandex Cloud, its public cloud platform, following the attacks. Updates from the maintenance team describe partial availability despite the outage indicators. They suggest that some customers may be able to access certain features, such as Yandex Cloud Console and API, but availability remains inconsistent across the platform. In its most recent update, the company said: "The Yandex Cloud platform is still operating in a limited mode. Our specialists continue restoration work around the clock. The technical support team receives an increased number of requests, so the response time can be increased. "Our recommendations continue to be relevant. We recommend using alternative sites for hosting and reserving resources." Internet monitoring organization Netblocks reported that Yandex Cloud's network connectivity was at 30 percent of normal levels on October 11. Ukraine president Volodymyr Zelensky said the drone attacks were a response to Russia's own, which had targeted datacenters in Kyiv. The BBC reported that in September, Russian drone strikes targeted a business center in the capital city, killing four people and damaging a datacenter, which in turn resulted in around 100,000 households losing internet access. The attacks led to other knock-on effects, such as public transport boards not displaying information in Lutsk. Kyiv's attack on the Vladimir site on Sunday morning came hours after controversial comments from US president Donald Trump, who accused Zelensky of wanting "to make problems for the world" by continuing to attack Russian oil refineries. Trump went on to say that it was time for Ukraine to elect a new president after Zelensky said measures should not be taken that allow Russia to generate more revenue to fund its war. Zelensky was referring to a deal between Trump and Putin to release diesel from Russia to the US and the rest of the world. Later that day, the US president claimed Russia and Ukraine had agreed to an "energy ceasefire" to halt attacks on each other's energy infrastructure. Kyiv said it was unaware of the agreement before Trump announced it on his social media platform, but was willing to halt attacks on Russian energy infrastructure if Moscow reciprocated. Russia launched a missile attack on a Ukrainian power plant hours later. ®

  •  

Aggiornamenti di sicurezza per LibreOffice

Aggiornamenti di sicurezza per LibreOffice sanano 6 vulnerabilità, di cui 1 con gravità "alta" che interessa LibreOffice Calc, applicazione della suite open source dedicata alla gestione dei fogli di calcolo. Tra queste si evidenzia la CVE-2026-63277 per la quale risulta disponibile un Proof of Concept (PoC) in rete.
  •  

Risolta vulnerabilità in MikroTik RouterOS

Aggiornamenti di sicurezza per MikroTik RouterOS sanano una vulnerabilità con gravità "alta". Tale vulnerabilità, qualora sfruttata, potrebbe consentire a un utente malintenzionato remoto autenticato di eludere i meccanismi di sicurezza ed elevare i propri privilegi sui sistemi interessati.
  •  

Bring Your Own Agent: Your Employees' Assistants Are Already Logged In

The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year

  •  

Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports

Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller. On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in losses totaling more than $86

  •  

Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the appliance to issue requests on their

  •  

Aggiornamenti di sicurezza Samsung

Samsung ha rilasciato aggiornamenti che sanano diverse vulnerabilità di sicurezza, di cui 7 con gravità “alta”, relative a dispositivi Samsung Mobile e a Samsung Continuity Service per Windows. Tali vulnerabilità, qualora sfruttate, potrebbero permettere a un utente malintenzionato di eludere i meccanismi di sicurezza e di eseguire codice arbitrario sui sistemi interessati.
  •  

Risolte vulnerabilità in MariaDB

Risolte molteplici vulnerabilità, di cui 3 con gravità "critica" e 8 con con gravità "alta", in MariaDB Server, noto database relazionale open source compatibile con MySQL, ampiamente impiegato per la gestione di dati strutturati in applicazioni web e ambienti enterprise.
  •  

OpenPrinting CUPS: disponibile PoC pubblico per la CVE-2026-107886

Disponibile una Proof of Concept (PoC) per lo sfruttamento della CVE-2026-107886 - già sanata dal vendor - presente in CUPS, piattaforma open source per la gestione dei servizi di stampa in ambiente Unix e Linux. Tale vulnerabilità potrebbe consentire ad un utente locale con privilegi elevati di compromettere la disponibilità del servizio sui sistemi interessati.
  •  

Framagenda / DAVx5 (android) - impossible d'accéder au service

Bonjour,

Je n’arrive pas à lier DAVx5 et mon calendrier FRAMAGENDA.
Je reçois l’erreur "Aucun accès possible au service CalDAV ou CardDAV.

J’ai un pixel 8, sous android 17.

J’utilise la double authentifications pour l’accès à Framagenda.

Voici comment je configure DAVx5

url de base https ://framagenda.org/remote.php/dav/

j’ai aussi essayé : https ://framagenda.org / http ://framagenda.org/remote.php/dav/ / http ://framagenda.org

(sans les espaces entre « https » et « :// »)

Nom d’utilisateur : J’ai essayé avec mon nom d’utilisateur ainsi que mon adresse mail

Mot de passe : mot de passe d’application (aussi le mot de passe du compte FRAMAGENDAS, sans succès). En désactivant la double authentification, cela ne marche pas non plus.

Vous avez une idée du problème ? (j’ai déjà regardé sur le forum, je n’ai pas réussi non plus avec les solutions proposées)

D’avance merci.

3 messages - 2 participant(e)s

Lire le sujet en entier

  •  

Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The

  •  

Aggiornamenti di sicurezza per prodotti MongoDB

MongoDB ha rilasciato aggiornamenti di sicurezza per sanare molteplici vulnerabilità, di cui 4 con gravità "alta" in Go Driver e nella libreria libmongocrypt. Tali vulnerabilità, qualora sfruttate, potrebbero consentire a un utente malintenzionato, in determinate condizioni, di compromettere la disponibilità del servizio sui sistemi interessati.
  •  

CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records

Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine. The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic's Claude Code, has been attributed

  •  

Risolte vulnerabilità su GitLab CE/EE

Rilasciati aggiornamenti di sicurezza che risolvono 24 vulnerabilità, di cui 1 con gravità “critica” e 5 con gravità “alta”, in GitLab Community Edition (CE) ed Enterprise Edition (EE). Tra queste si evidenzia la CVE-2026-97229 per la quale risulta disponibile un Proof of Concept (PoC) in rete.
  •  

Risolta vulnerabilità in Docker Desktop

Aggiornamenti di sicurezza risolvono una vulnerabilità con gravità “alta” in Docker Desktop per Windows, applicazione per eseguire e gestire container Docker sui sistemi Windows. Tale vulnerabilità potrebbe consentire a un attaccante di eseguire codice arbitrario con privilegi elevati sui sistemi interessati.
  •  

Google Gemini e i limiti gratuiti: cosa cambia davvero per te?

Google Gemini e i limiti gratuiti: cosa cambia davvero per te?

I limiti gratuiti di Google Gemini stanno per cambiare. Se utilizzi l'intelligenza artificiale di Google, questa è una notizia che ti riguarda da vicino.

Recentemente, l'azienda ha introdotto una novità significativa per la versione gratuita del suo chatbot AI: una modalità automatica. Questo sistema gestisce i modelli linguistici in base alla complessità delle tue richieste.

Ma cosa significa in pratica? Scopriamolo insieme.

Cos'è la nuova modalità automatica di Gemini?

Fino a oggi, la versione gratuita di Gemini si affidava principalmente al modello Gemini 1.0 Pro. Ora, il sistema diventa più intelligente. Google ha implementato una modalità automatica che agisce come un direttore d'orchestra per l'intelligenza artificiale. In pratica, Gemini analizza la tua domanda (il "prompt") e decide in autonomia quale modello utilizzare. Per richieste semplici, come chiedere una ricetta o il riassunto di un breve testo, potrebbe usare un modello più piccolo e scattante. Se invece la tua richiesta è più complessa, come scrivere codice o analizzare un dataset, attiverà il più potente Gemini 1.0 Pro. L'obiettivo è offrirti sempre la risposta migliore, bilanciando prestazioni e risorse.

Quali sono i veri limiti gratuiti per Google Gemini?

Con questa novità, arrivano anche limitazioni più chiare sull'uso del servizio. Sebbene Google non abbia fornito numeri precisi, ha confermato che la versione gratuita avrà dei limiti di utilizzo giornalieri e, potenzialmente, orari. Questo non significa che il servizio diventi inutile. Significa che è pensato per un uso "normale" e non per sessioni di lavoro estremamente intense. Puoi imparare a fruttare al meglio questa AI, anche con le nuove limitazioni, leggendo il nostro approfondimento.

Questi limiti gestiscono l'enorme carico sui server e garantiscono un'esperienza fluida a tutti. Se dovessi raggiungere la soglia, Gemini ti avviserà, invitandoti a riprovare più tardi.

I limiti gratuiti di Google Gemini nel dettaglio

Cosa succede quando si parla di limiti nella versione gratuita di Gemini? Ecco i punti chiave da tenere a mente:

  • Limiti sull'intensità: non si tratta di un blocco su determinate funzioni, ma sulla quantità di richieste che puoi fare in un dato arco di tempo.
  • Limiti dinamici: le soglie non sono fisse. Potrebbero variare in base al traffico generale sulla piattaforma per mantenere il servizio stabile e performante.
  • Nessuna sorpresa: se raggiungi il limite, un messaggio ti informerà della situazione senza bloccarti all'improvviso.
  • L'alternativa a pagamento: per chi necessita di più potenza senza limiti, la soluzione è Gemini Advanced. Offre accesso al modello Ultra 1.0 e una capacità di elaborazione superiore.

Cosa significa per l'utente medio?

Per la maggior parte delle attività quotidiane, probabilmente noterai pochi cambiamenti. Infatti se usi Gemini per scrivere email, fare brainstorming o chiedere informazioni, l'esperienza resterà ottima e gratuita. La modalità automatica potrebbe persino renderla più veloce per le domande semplici.

I limiti si faranno sentire soprattutto per gli "heavy user": sviluppatori, scrittori che generano lunghi testi o ricercatori. Per loro, le conversazioni lunghe e le sessioni di lavoro intense potrebbero essere interrotte, spingendoli a considerare l'upgrade a Gemini Advanced.

Gemini gratuito è ancora valido?

La risposta è un deciso sì. Gemini gratuito non solo rimane uno strumento potentissimo, ma con la nuova modalità automatica diventa anche più efficiente. Google sta semplicemente tracciando una linea più netta tra un uso occasionale e quello professionale intensivo. Quindi, non preoccuparti. Continua a esplorare le potenzialità di Gemini, con la consapevolezza che i suoi limiti sono pensati per garantire un servizio equo e accessibile a milioni di persone.

L'articolo Google Gemini e i limiti gratuiti: cosa cambia davvero per te? proviene da sicurezza.net.

  •  

Risolte vulnerabilità in SmarterMail

Rilevate 3 nuove vulnerabilità, di cui 2 con gravità “alta”, in Smarter Mail, piattaforma di collaborazione web sviluppata da SmarterTools. Tali vulnerabilità, qualora sfruttate, potrebbero consentire a un attaccante remoto autenticato di elevare i propri privilegi e di eseguire codice arbitrario sui sistemi interessati.
  •  

Khrys’presso du lundi 12 octobre 2026

Comme chaque lundi, un coup d’œil dans le rétroviseur pour découvrir les informations que vous avez peut-être ratées la semaine dernière.


Tous les liens listés ci-dessous sont a priori accessibles librement. Si ce n’est pas le cas, pensez à activer votre bloqueur de javascript favori ou à passer en “mode lecture” (Firefox) ;-)

Brave New World

Spécial IA

Spécial Israël

  • Israel demolishes properties of Palestinian who saved 30 Israelis on 7 October (middleeasteye.net)

    Yousef Zyadna was praised for rescuing Israelis during the 7 October attacks. Three years later, authorities have demolished properties belonging to him and his family

  • Bardella, l’antisémitisme et Israël (politis.fr)

    En soutenant le président du RN, un ministre israélien nous dit surtout quelle est la nature idéologique du gouvernement Netanyahou. Israël met aujourd’hui en danger les juifs du monde entier. Raison de plus pour ne pas identifier l’antisionisme, critique de la politique coloniale d’Israël, à un antisémitisme, et ne pas sommer les juifs de France à prendre position, dans un sens ou dans l’autre, dans le conflit israélo-palestinien.

Spécial femmes dans le monde

RIP

Spécial France

Le LOL de la semaine

Spécial femmes en France

Spécial médias et pouvoir

RIP

Spécial emmerdeurs irresponsables gérant comme des pieds (et à la néolibérale)

Spécial recul des droits et libertés, violences policières, montée de l’extrême-droite…

Spécial résistances

Spécial outils de résistance

Spécial MAGAM et cie

Les autres lectures de la semaine

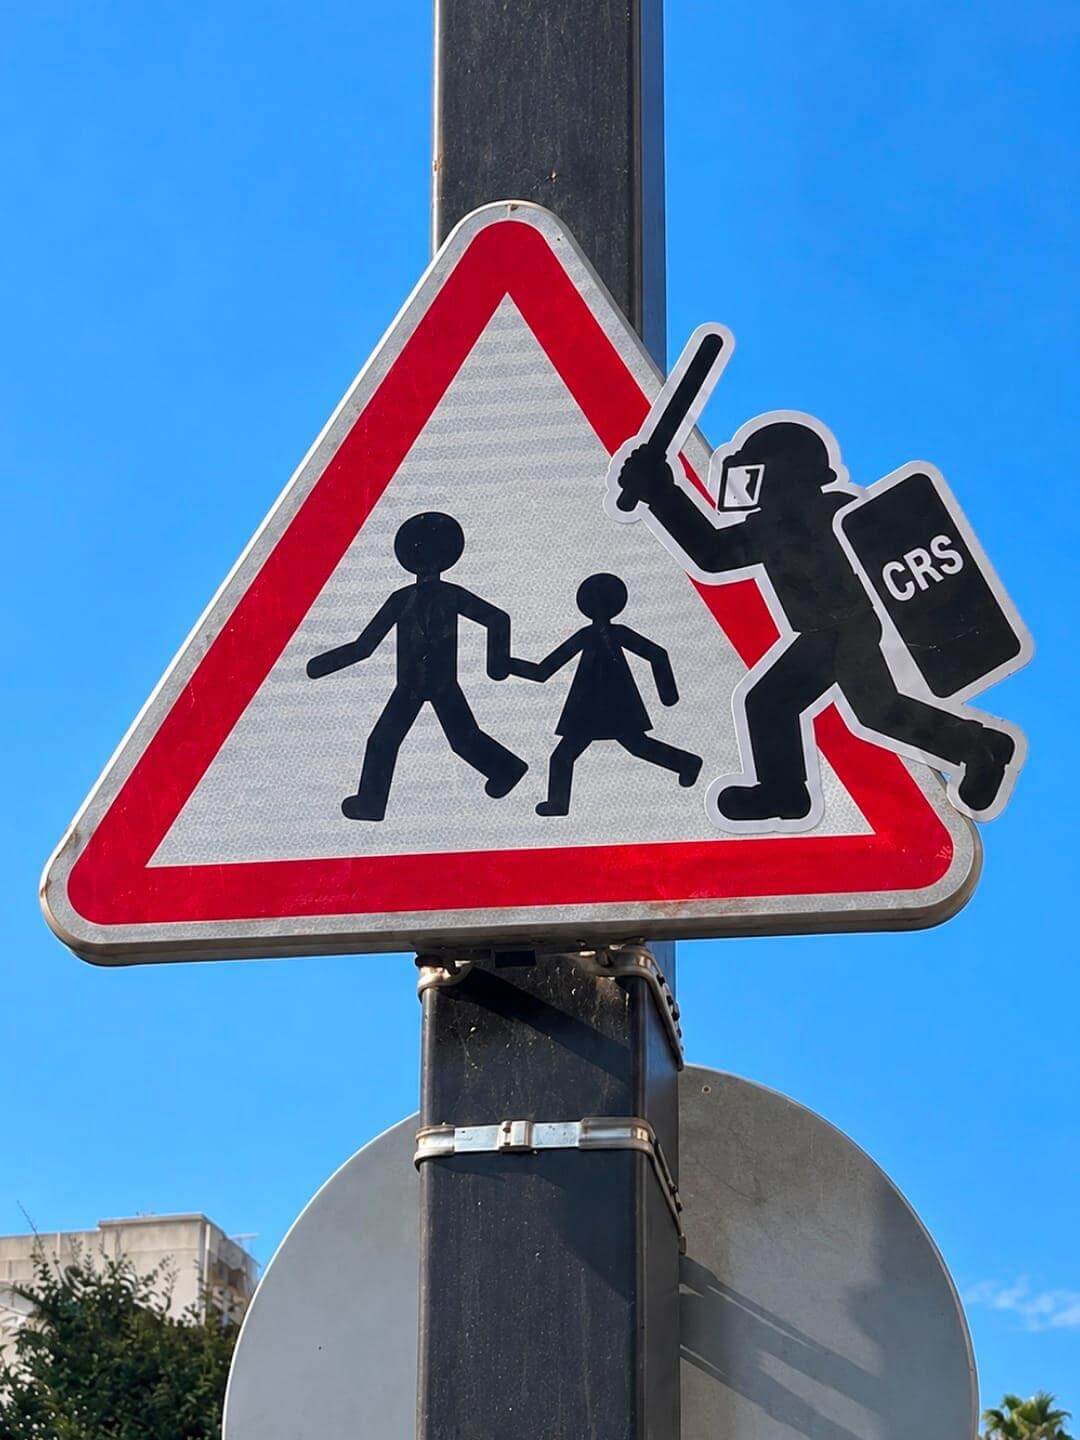
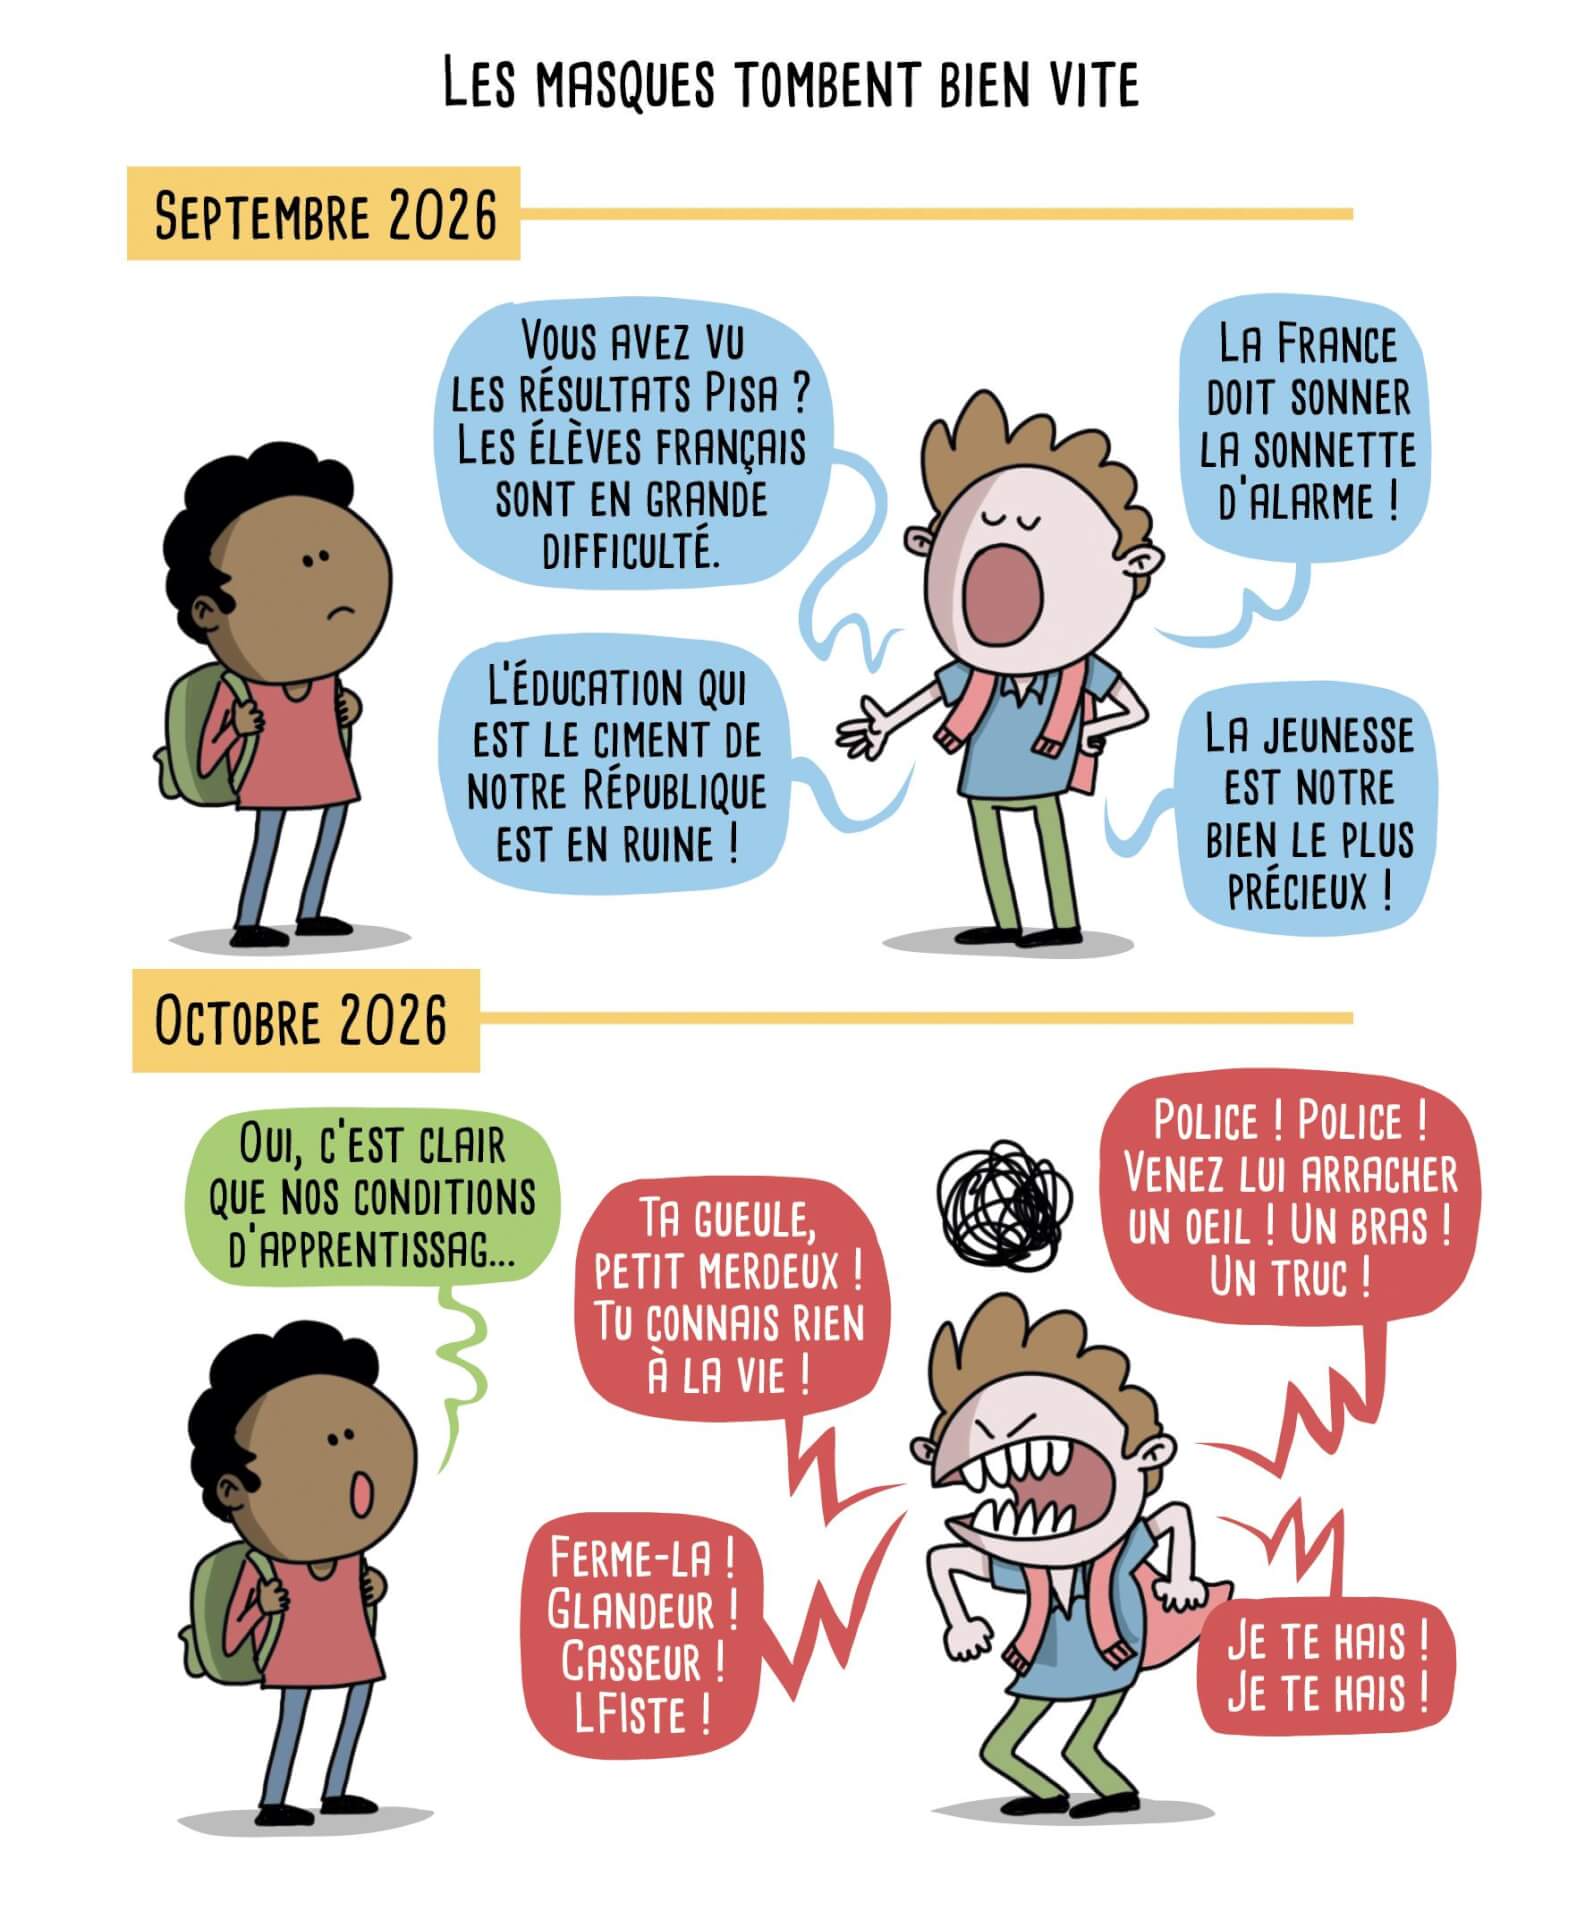
Les BDs/graphiques/photos de la semaine

Les vidéos/podcasts de la semaine

Les trucs chouettes de la semaine

Retrouvez les revues de web précédentes dans la catégorie Libre Veille du Framablog.

Les articles, commentaires et autres images qui composent ces « Khrys’presso » n’engagent que moi (Khrys).

  •  
❌