❌

Modalità di lettura

Will New Documentary Make Theranos Founder Elizabeth Holmes More Sympathetic?

TechCrunch writes: "Isn't it weird that I, like, did a TV show about kind of a business scam, and you got in trouble for like ... a business scam?" comedian and filmmaker Nathan Fielder gently asks Elizabeth Holmes. One month before the notorious Theranos CEO surrendered to begin her 11-year criminal fraud sentence in 2023, Holmes and her husband contacted A24 as a last-ditch effort to exonerate her in the public eye, suggesting they send a film crew to document her final days of freedom. Alongside director Lance Oppenheim, Fielder — a cringe-comedy mastermind whose work often walks the line between fact and fiction — embraced the impossible project of figuring out who the infamous Stanford dropout really is. "I never actually made that connection," says Holmes. "I think it's a pretty different situation...." We already know that Elizabeth Holmes is not innocent. What we still can't figure out, though, is whether she really, truly believes she did nothing wrong. Even as she sat on trial — listening to testimonies from investors who lost hundreds of millions of dollars, whistleblowers who were silenced when they flagged that Theranos' blood-testing devices didn't work, and patients who acted on incorrect blood test results — Holmes never wavered. Business Insider says the scariest thing about the new documentary "is how much I wanted to believe her." SFGate calls it "one of the finest works of journalism I've ever seen." As Fielder ingratiates himself with Holmes and [her husband] Evans, he gets them comfortable enough to ask the hard questions: about Theranos, about prison, and even about themselves. The resulting footage is often shocking. You will see Elizabeth Holmes, who still maintains she did nothing wrong, answer "no" when Fielder asks her if she's ever lied in her life... [Y]ou will also see Holmes and Evans spend a great deal of time in this movie attempting to boot up Theranos 2.0. They even go so far as to drag out some of the original Theranos blood testing apparatus, which looks like a bunch of random parts from TigerDirect they hooked together, to show Fielder what their product can do. We do not see it doing anything on screen, but the couple assures that it we would if it was, like, hooked up properly. These scenes are extremely funny, but funny isn't what Fielder is looking for. He's trying to figure out if this woman is a clueless naif, if she believes her own lies, or if she is playing the character of an innocent woman, and doing so with such effectiveness that, to paraphrase Fielder, she might be the most manipulative person in the world. The answer proves fabulously elusive, and so Fielder and Oppenheim go to extremes in their attempt to find it. They hold the camera on Holmes' rubbery elfin face for what feels like hours at a time, to see if she'll blink (figuratively or literally!). They interview Holmes' visiting parents, with the father, former Enron exec Christian Holmes, casually telling Fielder that everything changed for his daughter "when she was raped." To the furthest extreme, they bring in actress Amanda Seyfried — who played Holmes in the Hulu TV show "The Dropout" — to recreate any dialogues Fielder had with Holmes herself that couldn't be recorded on camera. Seyfried is so convincing in mimicking Holmes that you, the audience, might forget which scenes were Seyfried talking to the camera and not Holmes herself. I know I did. Continuing that theme in the film, TechCrunch notes, is how her husband Billy Evans "has constructed a lifelike AI avatar of his wife, trapped inside of a large vertical screen that he wheels over to the dinner table to sit with him and his kids as though she's actually there." Elizabeth Holmes "comes off in the doc as every bit as innately bizarre as anyone showing up for a cinematic freak show might hope," writes Variety: My personal hunch is that Fielder came away thinking Holmes is on the level, to the extent that someone who sometimes seems like an AI program's idea of how a human should behave can be on the level. There are a few possibilities that might explain how Holmes comes off the way she does in the movie: (a) She is a simpleton. (b) She is a conniving sociopath who happens to be utterly brilliant at playing a simpleton. (c) Somewhere between those poles, she is the very emblem of a woman who throughout her life has put herself in the sway of controlling men, to the detriment of her intellect, willpower and emotional development... Is it possible that the more you learn about someone, the less you might know how to think about them? Meanwhile, NBC News recently reported: Elizabeth Holmes, who was convicted of fraud for siphoning hundreds of millions of dollars from several high-profile investors, is scheduled to be transferred from a minimum-security federal prison to a halfway house next year, according to one of her victims... [America's Department of Justice "is required by law to notify victims of crime of case developments through letters and emails," the article points out.] She was sentenced in 2022 to 11 years and three months in prison. She and her business partner, Ramesh "Sunny" Balwani, were ordered to pay 12 victims a total of $452 million in restitution. Holmes has been serving that sentence at a minimum-security prison in Bryan, Texas. The halfway house will provide her greater freedom... In March, a judge cut Holmes' sentence from 135 months to 123 months. According to a court document, the judge agreed with Holmes that she did not personally cause "substantial financial hardship" to her victims. NBC News adds that a prison consultant they interviewed "said inmates who report to halfway houses can work, have phones, drive to religious services or shop for things they need and earn passes for weekends at home."

Read more of this story at Slashdot.
  •  

“La cronaca nera? A rimetterci sono i morti in vita. Garlasco il giallo perfetto, sia Stasi che Sempio potrebbero essere innocenti e il caso rimarrebbe irrisolto”: così Carlo Lucarelli

“Vedo un’eccessiva spettacolarizzazione che potrebbe logorare l’interesse del pubblico. I tempi lunghi sono suicidi per il true crime perché il pubblico si aspetta una verità finale in tempi ragionevolmente brevi come nei romanzi gialli dove c’è un Poirot che riunisce tutti in salotto, indica l’assassino e quello confessa. Qui ci vorranno anni per avere peraltro una verità solo giudiziaria”.

Così Carlo Lucarelli, scrittore e narratore storico della cronaca nera italiana, inquadra le dinamiche del caso Garlasco in un’intervista al Corriere della Sera. Un delitto che, sebbene tragicamente reale, possiede secondo l’autore elementi prettamente letterari: “I protagonisti del romanzo giallo ci sono tutti: Stasi il biondino dagli occhi di ghiaccio, Sempio il torbido, Lovati l’imprevedibile, personaggio straordinario”.

L'articolo “La cronaca nera? A rimetterci sono i morti in vita. Garlasco il giallo perfetto, sia Stasi che Sempio potrebbero essere innocenti e il caso rimarrebbe irrisolto”: così Carlo Lucarelli proviene da Il Fatto Quotidiano.

  •  

Uncle Scam Wants You … to cough up your cash and personal data, FBI warns ahead of midterms

The FBI is once again warning US citizens to be on the lookout for the scams that are so often rife around election season. With November’s midterms fast approaching, the FBI said scammers are known to use the names, imagery, and slogans of high-profile candidates for a range of frauds. These are often related to making donations and selling merchandise, but can also be geared toward stealing personal data for use in follow-on scams. And of course, more recently, fraudsters’ efforts can be all the more convincing given the rise in AI use and deepfake technology, which can also be used to more accurately imitate the likenesses of candidates and other officials. Campaign investment pool schemes are among the four big frauds the FBI wants the public to watch out for over the next few weeks. These involve scammers convincing their marks to pay into a campaign pool, which ostensibly pays out to all of those who donated after the candidate wins. More commonly, these types of pooled investment scams are based on collective investments into stocks and other appreciating assets. The FBI did not provide details about these campaign pools’ investment incentives or how victims are supposedly able to increase their stake by donating to the cause, but did say that no genuine campaign donations appreciate over time. Another common donation-based scam to be wary of is the one that convinces victims to fund a fake political action committee (PAC), one that collects supporters’ cash and promises to hand it to their favored party or candidate. Instead of forwarding money to a specific political campaign, however, the scammers pocket it all for themselves. Fraudsters are also known for claiming to sell merchandise related to political campaigns – orders that ultimately go unfulfilled. These constitute non-delivery scams, which rank in the top five genres of internet cons, according to the Internet Crime Complaint Center’s (IC3) most recent annual report. The same report put phishing at the number one spot in that same list, and the classic cyberattack features on the FBI’s list of midterm-related scams, too. Creating a sense of urgency, scammers will text victims claiming they have not yet registered to vote, and asking them to follow a link to a webpage where they can enter their details and complete the process, which of course leads to identity theft. While the FBI doesn’t include this detail in its advisory, Texans should be especially wary of these communication attempts given the recent computer issues that led to a massive backlog in registration applications. As of September 22, 226, around 600,000 applications were allegedly in limbo after a website flaw failed to record voters’ intentions to vote, and therefore did not receive registration forms from the Texas Secretary of State (SOS), according to a lawsuit [PDF] filed by voter registration organizations last week. However, spokesperson for the SOS’ office Alicia Pierce told USA Today that the backlog was only in the tens of thousands and that as of this week it was all-clear. Scammers may nevertheless continue to capitalize on the public awareness of the backlog when devising the lures for their phishing campaigns. The feds advised the public to be wary of these kinds of communications, and verify all political organizations, such as PACs, via the government’s election commission website. Although some scam PACs can appear on the website as registered, you can usually discern the suspicious ones when they report high expenses for matters such as consulting, fundraising, and other admin costs. The FBI's advisory follows separate action taken by X, which on Wednesday evening warned that influence campaigns originating from Iran, Russia, and China were targeting US voters, amplifying content across the political spectrum. The social media platform responded by nuking more than 13,000 accounts linked to the foreign interference attempts. ®

  •  

Ransomware gets personal: 'We-know-where-you-are kind of stuff'

Tim Beasley, a senior incident response consultant at Semperis, was investigating a cyberattack involving Russia’s Midnight Blizzard when a package containing nesting dolls and other regional gifts showed up on his doorstep. At the time, Beasley served as the lead investigator for Microsoft’s Detection and Response Team (DART). He assumed it was from the group, which has been linked to the Kremlin’s Foreign Intelligence Service (SVR), although the sender didn’t leave a note. “Just little souvenirs and gift basket stuff from that area of the world,” he told The Register. “We-know-where-you-are kind of stuff. It’s a real eye-opener when you get that type of thing.” While digital intrusions having physical consequences is nothing new, cybercriminals in recent years have turned to real-life harm and mental and physical trauma to force victims into paying extortion demands. Some groups even use cybercrime as a gateway drug to real-life violence. Over the summer, Europol and its partners' investigators flagged 4,340 “horrific” URLs for removal as part of an ongoing crackdown on The Com (short for community), a loosely knit network of online groups whose young members participate in a range of illicit activities including hacking, swatting, digital extortion, real-life shootings, and other physical violence. “We’ve seen violence as a service get used,” Beasley said. He’s also investigated ransomware attacks where C-suite executives receive pictures of their kids’ schools directly from the cybercriminals in an attempt to apply psychological pressure to pay the extortion fee. “I've seen threats involving people's families, from social media reconnaissance, and in our world you more and more come to expect it, which is unfortunate,” Beasley said. This type of psychological intimidation and harm against victim companies’ employees has seen an uptick in the last several years to the point where it's almost common. Thirty-seven percent of ransomware attacks involved psychological or physical threats against staff, according to Semperis’ annual ransomware risk report. The global study of 1,200 post-ransomware organizations conducted over the first half of the year found attackers threatening psychological intimidation (23 percent) and physical threats (17 percent), to force payment. They are not only targeting executives and staff, but also families of their victims. A quarter of these victims experienced doxxing – posting individuals' personal details, such as names, home and work addresses, and phone numbers online – while another 25 percent had to seek psychological and/or medical treatment in response to ransomware infections. Nearly the same number (24 percent) hired personal security teams, while 23 percent experienced swatting calls – that's when attackers phone emergency services and report a bogus incident like a bomb or active-shooter threat to trigger an armed response. Additionally, more than half (53 percent) of respondents reported that ransomware attackers carried through on threats in the past year. Some of these threats reported by ransomed organizations’ employees include: threatening texts, letters, or packages: 57 percent threats against family or friends: 37 percent physical intrusion: 19 percent abduction: 17 percent bodily harm: 13 percent stalking: 6 percent. “It's the more well-known groups,” using psychological and physical threats to force payments, Beasley said. “I've seen Scattered Spider, I've seen ShinyHunters, I've seen Lapsus$.” For what it's worth, ShinyHunters claimed in an exclusive interview with The Register that they “don't attack human beings.” They did, however, admit that “there are times in the work we do sometimes we have to push the corporate to the absolute limit to get them on the table.” The takeaway for defenders and executives from this report is to “stand your ground,” Beasley said. “Don’t buckle under the pressure, and just know that you know it's going to be okay. If you feel like you're under duress, then by all means get law enforcement involved. Don't be afraid to call the cops. Don't be afraid to get the FBI involved, sooner rather than later. And don’t pay them.” This last piece of advice is important, as once you pay, they're going to come back for more. Semperis’ report found that 69 percent of surveyed ransomware victims were targeted multiple times within the past 12 months, and 31 percent made multiple payments to attackers. “Don’t pay anything,” Beasley said. “Never pay them.”®

  •  

Owner of fashion brands Hobbs and Whistles joins autumn pwned collection

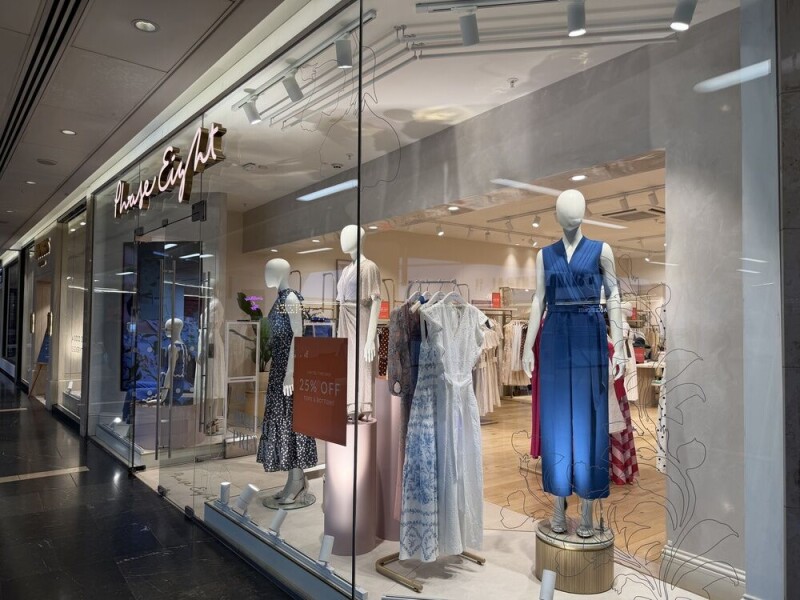
The owner of Hobbs, Phase Eight, and Whistles is the latest fashion retailer to suffer a cyberattack, leaving several IT systems offline and customers facing order delays. South African retail giant The Foschini Group (TFG) confirmed on Tuesday that its UK business, TFG London, discovered a cybersecurity incident on October 11 that affected all three brands. Two days later, several systems remain unavailable, and the company is still trying to establish whether any personal or sensitive information has been compromised. The incident hasn’t forced stores to close, but TFG said some website functions may be unavailable. Customers have also been warned that orders placed on or after Sunday could be delayed, according to an email seen by The Telegraph. "Stores are open as normal but some of our brand's website capabilities may not be available as the investigation continues," the company said. "We apologize for any disruption and will provide additional updates to our customers as appropriate." TFG said it immediately activated its incident response and business continuity plans, brought in external cybersecurity specialists, and notified the relevant UK authorities. A spokesperson at the ICO told The Register: “We can confirm we have received a breach report from TFG Brands (London) Limited and we are assessing the information provided.” There is at least some good news for shoppers worried about their payment details. In an email to customers, TFG London said a third-party provider handles payment processing and that, based on its investigation so far, it has no reason to believe payment information is at risk. Whether other customer data has escaped into the wild is another matter. TFG said it is still investigating that possibility and will notify affected individuals or organizations if it finds evidence of a compromise. The company has yet to disclose how attackers gained access, whether ransomware was involved, or when it expects to have its systems fully restored, and did not respond to The Register’s questions. The disruption appears to be confined to the three fashion brands. TFG said its White Stuff and Inside Story businesses are unaffected, as are its operations in Africa and Australia, which run on separate IT systems. The attack comes during a particularly miserable spell for fashion retailers, which seem to be attracting cybercriminals almost as enthusiastically as shoppers chasing a sale. Last week, ASOS customers received an unexpected notification informing them that the online fashion retailer had been hacked. ASOS subsequently confirmed that an attacker had gained access to an employee account by impersonating a trusted contact and obtaining login credentials. Armed with those credentials, the attacker got into third-party platforms holding customer names and contact details. Meanwhile, H&M is reportedly investigating claims that it was targeted by the notorious ShinyHunters cybercrime group. According to The Times, the Swedish fashion giant is examining allegations involving a limited amount of company data, although it stressed that it had found no indication its systems had been compromised. No evidence currently links the incidents at TFG London, ASOS, and H&M, and the latter has not confirmed a breach. Still, with three major fashion businesses linked with cyber trouble in little more than a week, October's hottest retail trend appears to be incident response.®

  •  
❌