Accedi
Android gets AI defenses against messaging scams, fake calls
15 Ottobre 2026 ore 21:48
Google announced new AI-powered defenses against scam messages and call-forwarding abuse on Android, currently rolling out to eligible devices. [...]

A phenomenon rarer than a solar eclipse and more powerful than any single storm system is unfolding this fall, and NASA is tracking it closely.
El Niño is a natural climate pattern that emerges roughly every two to seven years marked by warmer-than-normal water temperatures in parts of the equatorial Pacific. NASA scientists are keeping watch as it flips trade winds, redistributes ocean heat, scrambles rain patterns, and raises sea surface height across parts of the Pacific.
As of October, the National Oceanic and Atmospheric Administration (NOAA) has said that there’s an 83% chance that the strongest El Niño since 1950 is currently unfolding. People around the world, including farmers, firefighters, and coastal communities, are already experiencing the effects in different ways.
Follow along with these maps as NASA tracks El Niño from its epicenter in the equatorial Pacific Ocean.
One of the first clues appeared in satellite imagery in January 2026, when a swell of warm water called a Kelvin wave was spotted near Micronesia in the western Pacific. Kelvin waves are slow-moving pulses of water thousands of miles long. Like underwater freeways, they transfer heat from west to east across the Pacific. The warm water heats the air directly above it, making it rise. The change in air pressures weakens or even reverses the trade winds that typically blow in the opposing direction, from the Americas toward Asia, causing sea levels in the eastern Pacific to rise further, and waters to warm even more. This chain reaction signifies the start of an El Niño.
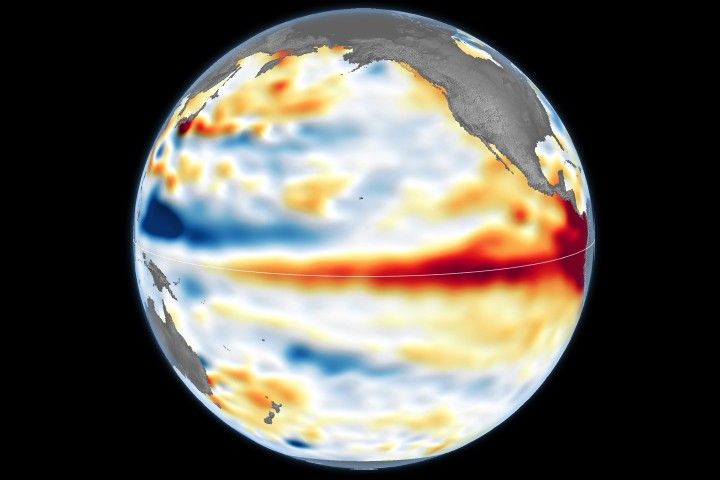
The map above shows that by early April, those Kelvin waves had reached the eastern Pacific, and sea surface temperatures had begun to warm. Warm water expands in volume, elevating local sea levels in some areas by as much as 1 to 1.3 feet (30 to 40 centimeters). The higher-than-normal water can be seen sloshing toward South America then moving up the coast to California. Sea levels that are six to eight inches (15 to 20 centimeters) lower than normal are visible around Indonesia and northern Australia.
“Kelvin waves are like the heartbeat of El Niño,” said Josh Willis, project scientist for sea level missions at NASA’s Jet Propulsion Laboratory in Southern California. “And our sea level satellites let us peer into the ocean and watch every beat.”
Scientists have used satellite altimetry to track the height of the ocean with ultraprecision since 1993. That unbroken data record continues today with the Sentinel-6 satellites. State-of-the-art radar altimeters aboard these satellites survey millions of square miles of ocean in a single day, complementing NOAA’s fleet of ocean sensors and buoys drifting and diving through the water below.
Warmer-than-normal seawater is one of the best-known indicators of El Niño. Already, sea surface temperatures in the eastern Pacific are about 3 degrees Fahrenheit (1.7 degrees Celsius) warmer than the long-term average and could jump another fraction of a degree in the coming months, Willis said.
Satellites carrying microwave and infrared radiometers can see through and around clouds to measure heat energy at the sea surface. Satellites in 2026 mapped the band of warmer-than-normal water as it expanded throughout the spring. The band, seen in dark red, stretches for millions of square miles from the heart of the Pacific to the coast of South America. Ocean temperatures can influence weather patterns around the world. Air above the water’s surface carries heat and moisture into the atmosphere, seeding rainstorms and rearranging weather patterns across the globe.
El Niño’s warm waters also change the color of the ocean. A NASA satellite is tracking these subtle shifts in hues, as equatorial Pacific waters have become measurably more blue over the last several months.
“Some people think of water as being just blue, but it’s amazing the multitude of colors the ocean can be,” said Matthew Kehrli, a lead research scientist for the PACE (Plankton, Aerosol, Cloud, ocean Ecosystem) satellite team at NASA’s Goddard Space Flight Center in Greenbelt, Maryland.
This spectrum is in part thanks to microscopic plants called phytoplankton, which form the basis of the marine food web. There are thousands of different species of phytoplankton, which come in shades like teal, brown, or green. This year, in areas of the Pacific Ocean along the equator that are typically lush with phytoplankton and greener as a result, these hues are waning.
This is an expected effect of El Niño. Phytoplankton thrive in cool, nutrient-rich waters, but during an El Niño, the weakening trade winds reduce the upwelling of nutrient-rich deep water to the ocean surface. With limited food supply, phytoplankton abundance drops. This decline can trigger cascading effects across the marine food web, forcing other marine life to relocate to new feeding grounds.
This year’s El Niño is the first since PACE launched in 2024, providing new views of the phenomenon. The Ocean Color Instrument aboard PACE observes the ocean in hyperspectral color — across several hundred different wavelengths of visible, near-infrared, and ultraviolet light — monitoring phytoplankton and other ocean-color changes in near-real time. With PACE data, researchers calculate the average color of the ocean, simplifying spectra of light into a single number, known as apparent visible wavelength.
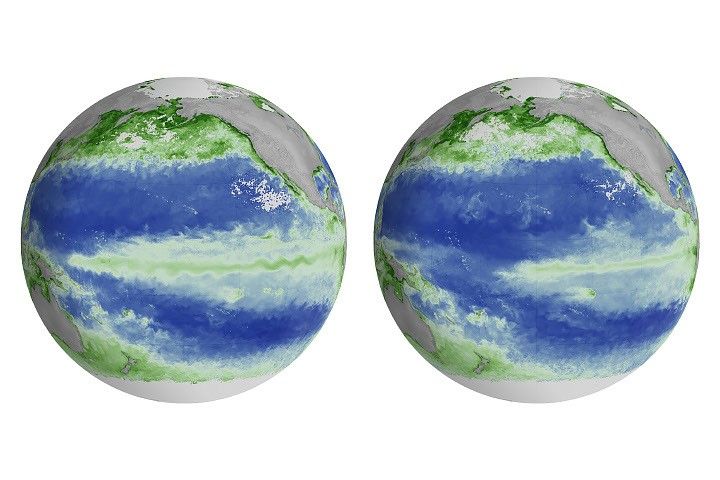
The 2026 map above shows the green area along the equator in the western Pacific Ocean shrink as a bluer shade fills in, indicating fewer phytoplankton. In contrast, the map from 2025 shows how the green-hued section stays steady over time.
“You have expectations of what you would think would happen,” Kehrli said. “But to visually see the results with the data products that you’re working with in real time is gratifying.”
NASA scientists will continue to monitor the signs and impacts of this El Niño with its fleet of Earth-observing satellites.
“El Niño touches almost all of us in some way every time it occurs,” Willis said. “While many have seen what it can do, we look to the ocean to understand why.”
View and download these data visualizations here.

Quando sei un libero professionista o un'azienda con partita IVA, la scelta del conto corrente è fondamentale per la gestione dell'attività. Molte banche e istituti finanziari offrono soluzioni specifiche per le partite IVA, con servizi e tariffe pensati per le loro esigenze
L'articolo Conto corrente per Partita iva, ecco i migliori 9 del 2026: costi, servizi e vantaggi proviene da Agenda Digitale.
Nelle grandi imprese entrano in media 21 nuove applicazioni SaaS al mese, ma il portafoglio resta quasi fermo. Il ricambio continuo, le integrazioni, l’AI e i modelli a consumo spostano così il problema dal numero delle licenze al debito operativo che l’organizzazione deve governare
L'articolo Debito operativo SaaS: il costo nascosto della velocità digitale proviene da Agenda Digitale.
La migrazione full cloud porta server, applicazioni, strumenti di collaborazione e backup fuori dall’azienda, sostituendo l’hardware locale con servizi gestiti. Un passaggio che promette costi più prevedibili e maggiore continuità operativa, ma impone scelte precise sul controllo dei dati e dei fornitori
L'articolo Full cloud per le aziende: vantaggi e condizioni per migrare tutto l’IT proviene da Agenda Digitale.
When teams consider deploying Kubernetes, one of the first questions that arises is: where should it run? The default answer is often the public cloud, thanks to its flexibility and ease of use. However, a growing number of organizations are revisiting the advantages of running Kubernetes directly on bare metal servers. For workloads that demand maximum performance, predictable latency, and direct hardware access, bare metal Kubernetes can achieve results that virtualized or cloud-hosted environments simply cannot match.
Virtualization and cloud abstractions have delivered convenience, but they also introduce overhead. By eliminating the virtualization layer, applications gain direct access to CPUs, memory, storage devices, and network interfaces. This architectural difference translates into tangible benefits:
Bare metal provides power and control, but it comes with its own challenge: managing servers at scale. This is precisely where Bare Metal as a Service (BMaaS) steps in.
metal-stack is an open-source platform that makes bare metal infrastructure as easy to consume as cloud resources. It provides a self-service model for physical servers, automating provisioning, networking, and lifecycle management. Essentially, it transforms racks of hardware into a cloud-like environment—while retaining the performance advantages of bare metal.
Key capabilities of metal-stack.io include:
By using metal-stack.io, organizations don’t need to compromise between the raw speed of bare metal and the automation of cloud infrastructure—they can have both.
Deploying Kubernetes on bare metal requires assembling several components into a complete ecosystem. With metal-stack at the foundation, additional layers ensure resilience, security, and operational visibility:
This layered approach turns bare metal clusters into production-ready platforms capable of handling enterprise-grade workloads.
Bare metal Kubernetes shines in scenarios where hardware performance and low latency are non-negotiable. Some standout use cases include:
In each of these cases, bare metal Kubernetes provides both the performance edge and the flexibility of modern orchestration.
For organizations interested in exploring this model, the path forward is straightforward:
This incremental approach reduces risk and allows teams to build confidence before moving critical workloads.
Running Kubernetes on bare metal delivers unmatched performance, efficiency, and control—capabilities that virtualized and cloud-based environments cannot fully replicate. Thanks to open-source solutions like metal-stack.io, organizations no longer need to choose between raw power and operational simplicity. Bare Metal as a Service (BMaaS) extends the agility of the cloud to physical servers, enabling DevOps teams to manage Kubernetes clusters that are faster, more predictable, and fully under their control.
Ready to explore further?
For high-performance computing, latency-sensitive applications, and hardware-intensive workloads, Kubernetes on bare metal is not just an alternative—it is often the best choice.
The post Kubernetes on Bare Metal for Maximum Performance appeared first on Linux.com.
Authorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply chain attacks ever.
In a statement released today, the Australian Federal Police (AFP) said two men from Western Australia, aged 21 and 23, were arrested in connection with a “sophisticated cybercrime syndicate that allegedly created malicious open-source software to rob thousands of global businesses.”
The AFP did not name the defendants, but KrebsOnSecurity learned the 21-year-old suspect’s real identity in June, and has been communicating with him ever since. This story includes interviews with TeamPCP’s self-described spokesperson, and examines clues left behind by the TeamPCP leader that likely led to his undoing.
TeamPCP vaulted onto the cybercrime scene in late 2025, embedding malicious code in hundreds of open source software tools and extorting victims for profit. Members of the group made headlines by compromising corporate cloud environments using a self-propagating worm dubbed Shai-Hulud, which added malicious code to open source programs maintained by developers whose credentials at public code repositories like GitHub or NPM were phished or stolen.
Writing for Wired, journalist Andy Greenberg described TeamPCP’s core tactic as a kind of cyclical exploitation of software developers.
“The hackers gain access to a network where an open source tool commonly used by coders is being developed,” Greenberg wrote in May. “The hackers plant malware in the tool that ends up on other software developers’ machines, including some who are writing other tools intended to be used by coders. The malware allows TeamPCP’s hackers to steal credentials that let them publish malicious versions of those software development tools, too. The cycle repeats, and TeamPCP’s collection of breached networks grows.”
TeamPCP also has practiced something akin to cyclical recruitment. In May, the source code for the third iteration of Shai-Hulud was published online, and TeamPCP soon after launched a contest offering $1,000 in virtual currency to whichever participant could conduct the largest supply chain operation using the worm’s code. According to the contest rules, participants were scored based on the number of weekly and monthly downloads of packages they compromised — directly incentivizing them to target the most popular code libraries.

A screenshot of a message from TeamPCP’s Telegram account, announcing the supply chain hacking contest. Image: dataminr.com.
“TeamPCP has stated the competition is a recruiting opportunity and they intend to purchase all meaningful access harvested from participants’ campaigns,” the security firm Dataminr wrote. “The $1,000 XMR (Monero) prize is a recruitment floor and has been dismissed by the actor as ‘just like participation trophy,’ adding ‘if you find something good you will be paid way more,’ confirming the contest’s true function as talent identification and malicious access acquisition at scale.”
In March, TeamPCP executed a supply chain attack targeting AI infrastructure by compromising the code for LiteLLM, an open source AI gateway that connects users to more than 100 different large language models. A recent analysis by the security firm CloudSEK found TeamPCPs attack on LiteLLM harvested cloud service keys and other secrets from more than 2,500 organizations, including many of the world’s top technology companies.
In May, TeamPCP claimed credit for compromising at least 3,800 code repositories at the Microsoft-owned GitHub, after a GitHub developer installed a code extension that was compromised by TeamPCP’s malware.
Security experts say TeamPCP is less of a hacker group than an amalgamation of threat actors from multiple cybercriminal gangs who sometimes work together toward similar goals.
“It is not a structured criminal crew with a single operator,” said Austin Larsen, a principal threat analyst with the Google Threat Intelligence Group. “It is a peer community of individually-skilled actors, with one clear center of gravity.”
That center of gravity is George Prepakis, an accomplished security researcher and self-described exploit developer who operates the Twitter/X profile @kernelstub. Earlier this year, @kernelstub tweeted a public invite link to a Matrix chat server he created and dubbed “Cybercats,” and TeamPCP and several other cybercrime entities have been using this server to communicate daily for the past several months.

A screenshot of the Matrix chat server “Cybercats,” whose members used hacker handles associated with multiple distinct cybercrime groups that have occasionally collaborated on a series of supply chain and data ransom attacks over the past nine months.
Kernelstub, like other administrators in the Cybercats chat, has been using his Twitter/X profile name as his handle in these Matrix communications, frequently tweeting references to other members and to conversations taking place in the Cybercats chat. In a number of cases, the corresponding X accounts for members of the Cybercats chat taunted cybercrime victims publicly before the incidents were reported in the news media.
The Cybercats administrator listed at the top of the screenshot above — “Boxturtle” — is a close associate of TeamPCP who has been tweeting about the group’s conquests under the name @xpl0itrsturtle. This handle corresponds to a data breach broker active on Breachforums and Darkforums who has been selling data stolen in a wave of recent breaches at automobile manufacturers, including BMW Group, Audi, Honda, Mercedes-Benz, Volvo and Toyota, as well as data allegedly taken from Snapchat and SportRadar.

The data leak site for the extortion group or handle “xpl0itrs.”
The Cybercats administrator “SeesawSec” in the screenshot above is the alias of whoever is behind the cybercrime group known as Fulcrumsec, which recently claimed credit for data extortion attacks against the pharmaceutical giant Novo Nordisk, the data broker LexisNexis, and Avnet, a Fortune 500 distributor of electronic components.

The data leak site of Fulcrum Security, a.k.a. Fulcrumsec.
The Cybercats administrator “@pcpcasper” also has been using a similar name on X to discuss TeamPCP’s attacks and victims. This person has an extensive message history on Telegram, where their messages and shared videos show @pcpcasper is an active and vocal member of the National Socialist Network, a neo-Nazi political organization based in Australia.
At one point in these chats, @pcpcasper shared videos and images of what they claimed was their cat, and several of those videos place this user in Western Australia. One source close to the investigation told KrebsOnSecurity that @pcpcasper was one of the two arrested, a claim supported by messages that @kernelstub posted online this morning.
The Cybercats member roster pictured above also features an administrator with the username “T,” which is short for the now-banned Twitter/X profile @pcpcats, the account operated by the self-described TeamPCP spokesperson who was arrested today. As we’ll see in a moment, @pcpcats also is from Western Australia.
By the time @kernelstub tweeted a public invite link to the Cybercats Matrix server, T/@pcpcats was posting only infrequently to the group chat, with other members often inquiring as to his whereabouts and well-being. The group’s collective concern related to @pcpcats’s tendency to blame his increasingly extended absences on the use of hallucinogens and other narcotics that kept him awake for days on end, but also caused him to crash in bed for several days after the highs wore off.
The Cybercats member @pcpcats has used multiple nicknames on the cybercrime forums, including EllisD25/LSD on Darkforums, BulkDMT on Breachstars, and Express on Breachforums. These accounts are linked because they all advertised the same Tox ID and/or Session ID as instant message contact handles in their cybercrime forum posts. BulkDMT was also known on the forums as DMT Host, which was a virtual private server (VPS) hosting service that was peddled on Darkforums and Breachstars.

DMT Host/EllisD25, posting on the English-language cybercrime community DarkForums in September 2025. Image: ke-la.com.
According to the cyber intelligence firm Intel 471, Express registered on Breachforums using the email address shitstickpp@gmail.com. Intel 471 finds Express posted on Breachforums across a two-month period in 2025 using four different Internet addresses located in South Africa. On July 30, 2025, Express announced on Breachforums they were selling access to 14 gigabytes of data stolen from South Africa’s State Information Technology Agency.
The threat intelligence platform Flashpoint recorded more than a year’s worth of messages from the TeamPCP leader’s alter ego on Telegram — Persy_PCP — who claimed they split their life living between two countries [full disclosure: Flashpoint is an advertiser on this blog]. “I have these [files] as well, problem is these are in another country,” Persy_PCP explained to another user inquiring about a stolen data set in November 2025.
Later that month, Persy_PCP complained, “My whole country is racist and they want people like me dead.” Flashpoint records show BulkDMT shared in September 2025 that “this country is going to fucking starve when they take the farmers land,” a likely reference to white landowners in South Africa who claim to be targeted by an ongoing genocide campaign.
This tracks with public reporting on TeamPCP. Cyberscoop reported in June that Google had traced TeamPCP’s residential and mobile Internet address connections to South Africa, “indicating the primary operator was located there during at least some of its attacks.”
BulkDMT also shared on the group chat at Breachforums that they were recovering from an addiction to methamphetamine. “My life is kinda fucked rn [right now], but that’s fine and there isn’t really a point in pouring so much emotional energy into that fact, my parents had money but I unfortunately got really addicted to some things so I don’t get to benefit from that. As long as I continue to survive, stay sober, and move closer towards my goals that’s enough drive and meaning.”
The identity threat protection company SpyCloud finds shitstickpp@gmail.com shows up in the registration of an account called ChristmasSnow on the cybercrime community Raidforums in 2022. Nearly all of the Internet addresses used to access that account came from ISPs in Perth, Australia, SpyCloud found.
KrebsOnSecurity looked up all of those Perth IP addresses in passive DNS records maintained by DomainTools.com, and found one of them — 211.27.196.111 — for several years was used as a private file server by a family in Perth with the last name of Thomson. Those records show at least three hosts — ithomson.direct.quickconnect.to (a remote Synology server), kthomson0061.direct.quickconnect.to, and joshuawthomson39.myqnapcloud.com (a QNAP network storage device) — persisted at that address between 2022 and 2025.
Searching on “joshuathomson39” in the breach tracking service Constella Intelligence reveals an account at the freight forwarding company kwe.com created in the name of Joshua Thomson from Perth, Australia. The open source intelligence platform Epieos finds the phone number attached to that kwe.com account was used to register a Facebook profile for Josh Thomson, which says his family includes a brother named Ruben, his father Ian, and his mom Cindy.
That Facebook profile also says Josh and his family are originally from Pietermaritzburg, in KwaZulu-Natal, South Africa, but currently living in Cottesloe, a beach-side suburb of Perth. A search in DomainTools for Ian Thomson and Australia unearthed five domains by the same registrant, including securecomputing.au, thomson.org.au, and thomsonfamily.net.au. Ian Thomson is a dentist in Cottesloe, and a biography says he graduated from The University of the Witwatersrand in Johannesburg, South Africa.
Constella finds a joshua@thomson.org.au registered a number of accounts online, but Josh doesn’t seem to have much of a connection to dodgy cybercrime forums. His brother Ruben, on the other hand, has quite the presence on these communities, dating back to at least 2018. Constella reports ruben@thomson.org.au frequently reused the password “joshuathomson1,” and Constella further finds that password was used by just a handful of accounts, including yolosolo17@gmail.com and surfinup8@gmail.com.
According to Intel 471, surfinup8@gmail.com was used to register the user Yolosolo17 on the crime forum Altenen in 2018, and that user account was registered from the Perth address 110.141.230.15. On Altenen, Yolosolo17 advertised free web proxies, as well as the domain rubenthomson.com, which was at one point used to sell steeply discounted iPhones. DomainTools says rubenthomson.com was hosted at 110.141.230.15 and registered to surfinup8@gmail.com.

A cached copy of the domain rubenthomson.com from 2017 shows a login page underneath a banded stack of money. Image: archive.org.
SpyCloud reports 10.141.230.15 was used by the email address sheepstealing@gmail.com on Raidforums and surfinup8@gmail.com on Nulled, and that the same IP was used by the email addresses ian@thomsonfamily.net.au, jasper@yakuza.cc, and rubenthomson1@gmail.com. SpyCloud also shows that sheepstealing Gmail address is tied to the accounts Sheep420, YoloSolo117 and Yakuza.cc on Raidforums, and to the account “Sheep Stealing” on Hackforums. Intel 471 says sheepstealing@gmail.com was used to register the account DingoFlour on Breachforums in October 2023, as well Sheepx on Altenen.
Epieos reports that ruben@securecomputing.au is tied to an Airbnb account for Ruben, who described himself as a Web developer who went to school at the University of Western Australia and was living outside the country. “Hey, I’m Ruben, my friends call me Ellis. I’m a Perth creative who occasionally books rooms when visiting family and for photography.”
Epieos also finds sheepstealing@gmail.com registered an upwork.com profile under the name Ruben, who said his main skills are setting up secure server hosting solutions and PHP full-stack Web development.
“I’m familiar with Linux, working with relational databases (SQL),” the Upwork profile reads. “I also script in Python mainly for writing social media bots.”

The Upwork profile for Ruben Thomson in Cottesloe, Australia.
Epieos further discovered sheepstealing@gmail.com is connected to a Microsoft account for Ruben Thomson, and to a now-defunct GitHub account called XmasSnow/XmasSnowisBack that scammed people on the forums in 2022 by claiming to sell exclusive exploits for recently-released software patches (recall that shitstickpp@gmail.com was used to register a forum account named ChristmasSnow).
This same sheepstealing email address registered a Twitter/X account in 2026 called “Gone Fishing” that lists its location as South Africa. That Gmail account also left several reviews for businesses listed on Google Maps over the past seven years, but all of those establishments are located on the west coast of Australia.

Business reviews in Western Australia left by the Google account sheepstealing at gmail.com.
The people search service Pipl finds a 21-year-old Ruben Thomson in Western Australia who has a phone number ending in 979. A lookup on that number at Epieos reveals it is connected to a TikTok account under the name Ellis, and to a PayPal account in the name of Ruben Thomson.
Finally, a search on the name Ruben Thomson from Cottesloe at the Australian government’s record of registered businesses finds he has incorporated or served as an official in multiple companies created since 2024, including Secure Computing Solutions, Tensor Industries, and another entity ironically named OPSEC Express. Recall that Express was BulkDMT’s nickname on Breachforums.

Australian companies connected to Ruben Thomson. Image: abr.business.gov.au.
It’s ironic because OPSEC is short for the term “operational security,” which refers to techniques and behaviors used to obfuscate and compartmentalize one’s real-life identity online, and using your cybercrime handle as part of your own company name is very much the antithesis of that practice.
There is at least one other major opsec failure by Ruben that exposed a link to TeamPCP. In June 2025, someone using the name Ruben Thomson registered on HackerOne, a popular “bug bounty” program that seeks to reward and recognize researchers who agree to work with affected software vendors to help fix the flaws before publishing about their findings. What was Ruben Thomson’s chosen HackerOne username? Deadcatx3, a nickname that has been flagged by multiple security firms as an alias used by TeamPCP.

The HackerOne profile for “Ruben Thomson” uses the nickname Deadcatx3, which multiple security firms have concluded is an alias used by TeamPCP. Image credit: flare.io.
In early July 2026, not long after having discovered clues about Ellis’s real life identity, KrebsOnSecurity interviewed the TeamPCP leader via Signal, where he was remarkably open about his activities and personal struggles [for the sake of simplicity, the TeamPCP spokesperson will be referred to from here on as Ellis].
Ellis claims he stopped doing cybercrime for TeamPCP in March 2026 — just before the attacks that compromised LiteLLM — and that at least one other individual has taken over the group’s leadership since then. Ellis shared that a year earlier he had just completed the latest in a series of detox and sobriety programs, and was two months sober when he reconnected with some old friends from the malware development scene.
“One year ago I needed help monetizing some [GitHub credentials], I was two months sober and needed a distraction and something to keep busy as well as people to speak to,” Ellis said. “I had largely disconnected from my old circle, they had become very toxic and I needed to get away from the substances. Previously I had done some mass exploitation campaigns and grew up doing [malware development] and [capture the flag] contests. There were some friends who were also vending but had stopped a while, and one of them introduced me to some chats where I posted access for sale.”
Prior to that, Ellis said, he was homeless and hopping between “some very unstable places.”
“Blackhatting is fun,” he said. “There are actual rewards and incentives to learn and you grow with your team. Without qualifications, no employer will even take the time to hear you out.”
Ellis claims he’s earned a grand total of about $20,000 for his activities with TeamPCP, and that it was never about the money or fame for him. Asked whether his experiences with TeamPCP might prepare him for gainful employment in a legitimate IT job, Ellis said he doubted it.
“I am nowhere close to a skill level where I am comfortable, and this would take maybe half a decade of further experience,” he said. “I no longer have to choose between rent and food for that I’m grateful and so are the team members.”
Ellis expressed no remorse over his cybercrime activities, and said he was grateful for the friendships and relationships built throughout his engagement with TeamPCP. The young hacker also seemed resigned to his fate, and told KrebsOnSecurity that he’ll accept the consequences if he’s ever arrested.
“If I’ve already been found out then its out of my control, I’ll make peace with that,” he said. “Honestly, I think someone like me needs a lot of help that prison just can’t provide. If I had the funds to study different parts of the field and closer guidance, this would have turned out differently. But that’s a pipe dream and we both know this.”
It is clear from reading Ellis’s posts to the group’s Matrix server chats that his struggles with sobriety are ongoing. On Thursday, June 25, Ellis told @kernelstub he was about to “trip” with his “homie.”
“What kind,” @kernelstub inquired.
“Ketty and some DMT,” Ellis replied, referring to the dissociative anesthetic ketamine and dimethyltryptamine (DMT), a powerful psychedelic compound that is found naturally in some plants but is also synthetically produced in underground lab environments. “There’s a little 2cb so we might throw that in the mix,” he continued, referring to another psychedelic compound by its chemical shorthand.
Roughly two weeks before his arrest, Ellis told KrebsOnSecurity he was ready to leave his life of crime behind and was prepared to turn himself in, but that in the meantime he was making plans to tie up loose ends.
Less than 24 hours later, the TeamPCP leader posted an image on Telegram showing a yellowish powdered substance in a baggie and on a scale, possibly synthetic DMT. The image shows the powder being weighed next to a series of small vape cartridges, two of which are open on the table in front of the photographer.

An image posted by the TeamPCP leader to Telegram, advertising his acquisition of some type of psychoactive substance, most likely a synthetic version of the powerful hallucinogen known as DMT.
The two defendants were arrested Wednesday morning. The AFP said the men face a combined 14 cybercrime offenses and are scheduled to appear in Perth Magistrates Court today.
Charlie Eriksen is a security researcher at Aikido Security who has closely followed TeamPCP’s cybercrime campaigns. Eriksen said TeamPCP are a good example of a new kind of threat actor that does not fit neatly into the usual categories.
“They are not a state actor, not quite organized cybercrime, and not purely ideological,” he said. “Their motivations seem to mix money, disruption, attention, and ideology.”
Eriksen said that historically there has always been a meaningful gap between reading about an attack technique and being able to reliably turn it into an operational campaign, but that large language models (LLMs) and artificial intelligence increasingly are helping threat actors to bypass that knowledge gap.
“You had to understand the research, adapt the code, troubleshoot it, build infrastructure around it, and then repeat that process across different targets,” he said. “LLMs have compressed that gap significantly.”
According to Eriksen, this creates an environment where threat actors suddenly have the ability to operate at significant scale without having developed the operational discipline that traditionally accompanies that level of capability. Put another way, it sets the stage for cybercriminals who are capable enough to cause significant damage, but not necessarily careful enough to understand or care about the consequences.
“They can be noisy, they can make mistakes,” he said. “They can leave evidence everywhere. They can take risks that a professional criminal group or intelligence service would consider completely unacceptable. But that does not necessarily make them less dangerous. In some ways, it can make them more dangerous.”
In a recent blog post, Eriksen called TeamPCP’s Shai-Hulud worm the “best thing to happen to supply chain security,” because it forced GitHub and other public coding platforms to erect new security safeguards.
In direct response to TeamPCP’s broad success at pushing poisoned versions of popular software packages, GitHub in late July introduced a three-day “cooldown” mechanism for Dependabot, the platform’s tool for auto-fetching newly shipped updates for any package dependencies. Cooldown periods are designed to help buy time for security tools and package maintainers to identify and remove any compromised versions. Other coding ecosystems like Python and various JavaScript platforms also added support for cooldown periods this year amid growing calls from security experts about the need for more widespread adoption of the safety feature.
Eriksen said TeamPCP’s legacy is that they achieved in the span of a few months what the supply chain security community has been unable to do for years.
“They managed to wake up Microsoft to the fact that they had become negligent in terms of security,” Eriksen said. “By compromising GitHub and stealing their source code, they humiliated Microsoft into action, making them finally act on what we had been asking them to do and take seriously for a while now.”
Update, 10:08 a.m. ET: A story this morning from ABC News in Australia confirms Ruben Ian Thomson of Cottesloe was one of the two arrested. The 23-year-old suspect thought to be @pcpcasper, Michael Gaebler, also was arrested in Perth. ABC News reports that Thomson was denied bail (Mr. Gaebler’s attorney reportedly did not request bail for his client), and that both men will be held in custody until their next court appearance on September 18.

Hai dei file a cui vuoi poter accedere facilmente da qualsiasi device? Li puoi caricare su NextCloud! Devi scrivere un testo assieme ad un’altra persona che vive lontano? C’é Etherpad! Vuoi inviare un file in modo riservato? Puoi usare Lufi! Ti serve una mappa online? Ma c’é OpenStreetMap! Vuoi condividere uno status ma solo con alcuni amici intimi? Puoi farlo con Friendica! Devi cercare qualcosa sul web? C’é SearX!
Insomma: chi te lo fa fare di usare servizi centralizzati il cui solo scopo é carpire informazioni su di te, se ci sono provider online che mettono a disposizione i migliori software open source?
La maggior parte degli utenti possiede dei device (smartphone, tablet, computer fisso o portatile…) ma non ha in casa un proprio server personale con cui gestisce ed archivia i propri contenuti. Questo perché esistono dei fornitori commerciali di servizi online (provider come Google, Apple o Facebook) che mettono comodamente e spesso “gratuitamente” a disposizione tutta quella serie di servizi che altrimenti bisognerebbe installare/impostare/aggiornare/riparare da sé. Affidarsi a provider esterni, dunque, a primo acchito risulta comodo perché libera dall’onere di imparare a gestire gli strumenti su cui si regge la propria vita digitale.
E’soprattutto nella seconda metà degli anni 2000 che si affermano i principali provider di servizi online. É in quel momento che si sviluppano aziende e strumenti come Dropbox, Evernote, Facebook, Google Docs, iCloud, Twitter, Whatsapp, YouTube ecc. Nel giro di pochi anni però, tramite acquisizioni e battaglie commerciali, la situazione che si é venuta a creare é che i principali servizi online sono proprietà di soli cinque colossi americani: Amazon, Apple, Facebook, Google, Microsoft.
Cinque aziende commerciali che hanno nelle proprie mani la vita digitale di ogni individuo del pianeta, alcune delle quali sono state fondate con l’esplicito scopo di raccogliere, analizzare e vendere tutte le informazioni che possono sui propri utenti.

Non tutti ci han fatto caso, ma mentre questi provider nascevano e si facevano ogni giorno più forti é avvenuto nelle nostre vite un importantissimo doppio cambio di paradigma. Il tutto é avvenuto in maniera esplicita, alla luce del sole e nient’affatto misteriosa, solo che é avvenuto tanto in fretta e con un tale hype nei confronti della “tecnologia del futuro” che la maggior parte delle persone non se n’é curata: 1) si é passati dallo “strumento come strumento” allo “strumento come servizio” ed alla 2) cessione volontaria dei propri dati sensibili in cambio dell’utilizzo di tali servizi.
Il concetto, insomma, é che si é passati dal “possiedo carta e penna su cui scrivo quel che mi pare e poi se voglio lo tengo chiuso in un cassetto oppure lo consegno a chi mi pare ma sempre senza dover render conto a nessuno della mia scelta” al “Posso usare la fantastica penna di lusso e la fantastica carta della ditta X per scrivere tutto quel che mi pare, alla sola condizione che la ditta X leggerà tutto ciò che scrivo e ne farà quel che vorrà”.

Tu, utente, non “hai” Whatsapp. Quando dici che “hai Whatsapp” stai dicendo una stronzata.
Non hai idea di quali informazioni su di te il software di Whatsapp trasmette ai server di Facebook(i millisecondi che sei stato fermo su una foto? se ne hai allargato un dettaglio? se l’hai salvata? se hai salvato una schermata con quella porzione di chat? quanti errori grammaticali fai? in quali ore dormi? quali sono le persone di cui cancelli le chat?).
Non sai in che modo questi dati vengono interpretati (il numero di emoji usati in relazione alle volte in cui usi certe parole? quali sono le parole che usi solo con certe persone? i tuoi riferimenti culturali più comuni in relazione con la mappa dei tuoi spostamenti? le opinioni che hanno su di te i tuoi “amici” e che si scambiano nei messaggi privati?).
Non sai in che modo Whatsapp ti profila (ha intuito che forse tra te e una certa persona c’é una tresca in base all’analisi dei vostri tracciati GPS ed ai messaggi fasulli che avete inviato? ha dedotto le tue debolezze emotive utilizzabili come grimaldello propagandistico da una forza politica che avversi per confonderti le idee?)
L’ultimo punto probabilmente é il più importante. Si sa, che spesso il problema non é in chi trasmette informazioni (tu), ma in chi le legge (Facebook). Se Facebook interpretasse dalla tua attività online che sei potenzialmente una minaccia per il governo in carica e questa informazione fosse venduta proprio a qualcuno che lavora per il governo in carica beh, a seconda della natura di tale governo potresti passare decisamente dei brutti momenti.
Possiamo girarci attorno finché si vuole, ma la verità é che l’unico software su cui puoi avere la massima fiducia é software FLOSS installato da te su un tuo device di proprietà, a cui solo tu hai accesso.
Idealmente, dunque, un web veramente libero dovrebbe essere composto da innumerevoli device e server personali su cui sono installati gli strumenti software che ognuno preferisce e per far sì che questo non porti ad una eccessiva frammentazione delle piattaforme, idealmente e pur mantenendo la propria indipendenza, queste dovrebbero comunque possedere un certo grado di interoperabilità (ad essempio costituendo una rete federata). Si tratta di uno scenario tecnicamente realistico, molto vicino a quello delle prime reti BBS all’alba di Internet e che qualcuno sta effettivamente cercando di far prender nuovamente piede. Gli strumenti ci sono e funzionano già a dovere. Quel che gli manca é solamente un’adozione massiccia.
Certo é pur vero che l’idea di fare self-hosting (ossia il possedere un proprio server personalizzato) può spaventare molte persone, nonostante gli strumenti per realizzarlo siano sempre più alla portata di chiunque (come ad esempio YuNoHost un sistema operativo pensato proprio per server casalinghi gestiti da un utente inesperto, già predisposto per ospitare un’Istanza Nextcloud, Matrix, Mastodon, XMPP, WordPress, SearX, Tiny Tiny RSS, Wallabag e praticamente tutto quel che riguarda la vita digitale di ognuno).
Capiamoci: siamo nel 2019; i computer esistono ormai da eoni, ma anche a voler restare stretti e concentrarci solo sul periodo in cui questi sono entrati in massa nelle case, stiam parlando comunque di 25-30 annima la conoscenza media di questi strumenti é perlopiù limitata all’utilizzo più superficiale. La situazione può essere paragonata allo scenario in cui milioni di automobilisti che, pur sapendo guidare, ignorassero totalmente cosa siano il motore, le pastiglie dei freni o la batteria, ma si accontentassero di sapere che girare il volante a sinistra fa girare a sinistra anche le ruote, credendo così di sapere come funziona un’automobile.
Il fatto é che, come già detto, siamo nel 2019: non si pretende certo che tutti diventino dei provetti meccanici-hacker, ma almeno che si diffonda una conoscenza generale giusto un minimo più accorta. Insomma: basterebbe che si sapesse che sotto il cofano c’é una cosa chiamata motore e più o meno in base a quali princìpi funziona.
La cosa ancor più drammatica é che le conoscenze base per potersi muovere in campo informatico (una spolverata di teoria, imparare ad installare un sistema operativo, compiere operazioni di maintenance, usare motori di ricerca come si deve ed alcuni concetto-base di sicurezza informatica) possono essere apprese con un corso di sette giorni, meno che per la patente, ma nonostante l’utilizzo dei device informatici sia una costante su base quotidiana per milioni di persone, ancora troppo poche hanno “fatto il corso di sette giorni”.

Come già esposto in altri articoli, esistono da anni diversi strumenti FLOSS (ossia software aperto, gratuito e liberamente utilizzabile) che non hanno nulla da invidiare ai loro corrispettivi commerciali. Anzi, in molti casi gli strumenti FLOSS sono pure tecnicamente più avanzati delle loro controparti, tanto che moltissimo software che utilizziamo quotidianamente (come Chrome o Whatsapp) non é che una versione modificata di software FLOSS. L’unica pecca del software FLOSS, semmai, deriva dal fatto che essendo utilizzao da meno utenti, spesso ha una quantità minore di contenuti: la quantità di roba che vien pubblicata sui social open durante una giornata equivale forse a quella che su Facebook vien pubblicato in un minuto. Di conseguenza vi é anche minor spinta a venir incontro agli interessi di un pubblico che si trova altrove. Si tratta della classica situazione del gatto che cerca di mordersi la coda: gli utenti non adottano un sistema se non ci son gran quantità di contenuti, ma non possono esserci gran quantità di contenuti se non ci sono utenti.
Per dirla in altro modo, tornando alla metafora automobilistica: finché tutti continueranno a voler usare ruote di legno, quel tizio strano che ha avuto l’idea di fare ruote di gomma resterà confinato nella sua bottega a fare le ruote di gomma una-ad-una per i suoi clienti affezionati, ma non riuscirà mai a metter su una fabbrica per produrle in serie. Questo a meno che non ci sia una forte spinta ad adottare in massa tali ruote di gomma, ma si tratta di una spinta che non verrà mai dalle grandi aziende produttrici di ruote di legno.

Una selezione di strumenti e piattaforme commerciali libere e la loro controparte commerciale
Una delle difficoltà maggiori riguardanti il software FLOSS é il riuscir a far capire il loro valore ad una popolazione che, come già detto, ha giusto delle vaghe conoscenze informatiche. Spiegare i vantaggi degli strumenti FLOSS a chi é privo di ogni base informatica spesso suona difficile come cercar di spiegare com’é possibile che gli aerei si librino nell’aria ad una popolazione vive nel terrore che la Luna caschi dal cielo.
Per esempio: quando si parla di privacy e protezione dei dati personali sul web, solitamente l’immagine che viene evocata dall’utente comune é quella del tizio parte-hacker-parte-007-parte-esattore-di-Equitalia che traffica sul web per carpire informazioni piccanti o spiacevoli sulla tua persona, ossia uno scenario da film complottista che, pur non essendo impossibile, nella maggior parte dei casi risulta alquanto improbabile: a chi mai interessa cosa faccia nella vita privata il signor Gino del quinto piano? Certo però che quelle stesse informazioni diventano estremamente interessanti se acquisibili in massa assieme a quelle di milioni di altre persone…
In realtà ciò che avviene nella maggior parte dei casi é che le informazioni dettagliatissime che hai fornito su di te vengono utilizzate all’interno dei cosiddetti big data per impostare argomentazioni politiche, saggiare il terreno su certi argomenti senza tener conto dello scarto fra vita reale e vita sul web e soprattutto, per modificare il discorso pubblico prevalente su determinate questioni.

Il tuo profilo, il tuo singolo profilo utente, di per sé ha scarso valore (a meno che tu non sia un VIP o un noto criminale). Ma se il tuo profilo fa parte di un bouquet di milioni di profili allora la cosa cambia!
Quel che avviene é che i committenti hanno modo di influenzare quali e quante informazioni riceverai, facendo sì che sui social certe notizie appaiano nella tua Timeline ma non in quella del tuo vicino o che ti venga suggerito si seguire certi contatti e non altri. Le informazioni che hai fornito su di te sono uno strumento impagabile affinché queste modifiche riescano ad essere cucite proprio apposta per te.
Non é un caso se milioni di persone vengono portate a credere a cose del tutto false o a consolidare idee che, se non ci fosse controllo sui contenuti che ricevono, non sarebbero difese con tanta irrazionalità. Chi manipola quel ti vien detto, non fa altro che indirizzare il tuo modo di pensare.
In poche parole, scegliere di utilizzare le grosse piattaforme centralizzate del data-mining (letteralmente “estrazione dati”, ossia ciò che fanno Facebook, Google ecc) equivale a buttarsi nel mare in cui viene effettuata la più imponente e specialistica pesca a strascico del mondo: una pesca a strascico smart che se da un lato coinvolge tutti i pesci nel mare, nessuno escluso, dall’altro non uccide i pesci, ma li lascia in acqua, studiandoli tanto a fondo da capire come fare a far sì che ogni singolo pesce poi nuoti nella direzione che il pescatore desidera.
In sostanza più informazioni personali forniamo alle grandi compagnie di data mining e più aiutiamo chi manipola le informazioni sui media mainstream; più aiutiamo chi vuole seminare odio in maniera mirata; più aiutiamo le società di marketing a renderci dipendenti dai loro prodotti. Un esempio su tutti? In Italia, da anni, il numero di crimini violenti é in calo costante. Non é una novità: ogni anno i quotidiani pubblicano i nuovi dati e da anni, appunto, si annuncia che sono calati rispetto all’anno prima. Eppure la percezione diffusa é che invece siano in aumento. Stessa cosa per il numero di stranieri residenti in Italia: oltre il 73% degli italiani ne sovrastima il numero. Certo, la percezione pubblica non viene modificata dai soli social, anche i media hanno un ruolo fondamentale in questo, ma é innegabile che oggi il grosso di questo lavoro avvenga proprio sui social.

I recenti scandali legati a Facebook, Cambridge Analytica, la Brexit,il Russiagate ed i sospetti di intervento esterno sui social durante diverse campagne elettorali non sono che l’aspetto più macroscopico e noto dell’intreccio fra big data, politica e manipolazione dell’opinione pubblica.
Ecco, tutto questo fa parte di ciò che l’utente medio fa fatica a vedere e tra un’app per mandare immagini di gattini con musichette carine ed un’app che fa lo stesso ma meno pubblicizzata e usata da meno utenti, sceglierà la prima, anche se la seconda ha caratteristiche migliori ed é più adatta a proteggerne le informazioni personali.
Socialità quantitativa e strumenti che necessitano apprendimento raso-zero sono, purtroppo, i fattori determinanti per la scelta delle piattaforme da utilizzare. Restando all’esempio automobilistico, é come dire che il mondo preferisce le auto senza specchietti, frecce, cinture di sicurezza ed altri dispositivi di protezione “perché é roba da nerd maniaci” e si é adattato a ritenere che beh, é normale che ogni automobilisca faccia qualche incidente e perda qualche arto.

Se proprio non si ha modo o voglia di self-hostare i propri strumenti software, un buon compromesso fra self-hosting ed il ricorso ai provider di servizi commerciali come Facebook o Google é quello di rivolgersi a dei provider online di software open source. In pratica, se Google mette a disposizione i suoi strumenti (Google Calendari, Contatti, Drive, Mail, Ricerca, Documenti, Fogli, Presentazioni, ecc…) ed anche Apple fa altrettanto con i propri (iCloud, Contatti, Pages, Numbers, ecc…), così come fa Facebook (Facebook, Messenger, Instagram, Whatsapp) e tutti quei provider che mettono a disposizione il proprio unico strumento (L’azienda Evernote mette a disposizione lo strumento Evernote, l’azienda Twitter mette a disposizione lo strumento Twitter ecc.) esistono anche diversi provider che invece mettono a disposizione applicazioni FLOSS che, se l’utente volesse, potrebbe tranquillamente scaricarsi e installare su un tuo server personale, essendo tutto software aperto e liberamente scaricabile (quindi, chiunque abbia le necessarie competenze tecniche, può verificare cosa fa davvero il software “sotto il cofano” e come).

La comodità di questa soluzione é indubbia: hai un server sempre attivo accessibile 24/24 che viene mantenuto efficiente, aggiornato e riparato da qualcun’altro cosicché tu possa accedervi senza problemi.
L’idea alla base dei provider di applicazioni FLOSS é che anziché esserci solo 4 o 5 colossali provider cui si rivolgono tutti, possano invece esserci centinaia, migliaia, milioni di server che offrono una vastità di strumenti che però siano compatibili tra loro o addirittura federati.

Una piccola digressione: Framasoft é un provider che fornisce una propria Istanza Mastodon, mentre Bida é un altro provider che fa altrettanto. Pur essendo due provider distinti (sotto un certo punto di vista é come dire Apple e Facebook) entrambi mettono a disposizione lo stesso strumento, Mastodon, che ha la peculiarità di essere federato. Ciò significa che gli utenti che usano l’Istanza Mastodon di Framasoft e quelli che usano l’Istanza Mastodon di Bida potranno interagire fra loro come se fossero su un’unica grande chat. Volendo fare un paragone, sia iChat che Whatsapp, i software di chat di Apple e Facebook, sono stati entrambi sviluppati in base ad XMPP, che é software FLOSS. Questo vuol dire che tecnicamente sarebbe semplicissimo far dialogare tra loro Whatsapp ed iMessage, ma ciò non avviene puramente a causa di bagarre commerciali.
A questo punto però sorge spontanea una domanda: perché non fidarsi di Facebook e Google ma fidarsi di un provider open source? Si tratta pur sempre di dover riporre fiducia in qualcuno che (presumibilmente) non si conosce ed a cui si affidano i propri dati personali. L’osservazione é in effetti corretta e l’unica risposta sensata é che così come non ci si può fidare dell’uno non ci si dovrebbe fidare nemmeno dell’altro.
Ma ci sono dei “ma”.
Innanzitutto i maggiori provider di servizi commerciali come Facebook e Google sono ESPLICITAMENTE basati sulla lettura, analisi e compravendita dei contenuti che noi forniamo. Da cosa guadagnano Facebook e Google? Qualcosina sì dalla pubblicità, ma il grosso dei guadagni, quello che ha rende Mark Zuckerberg uno degli uomini più ricchi del mondo, é la vendita delle informazioni degli utenti.

Gli strumenti messi a disposizione dai provider sono un’infinità e spaziano dagli strumenti per ufficio (scrittura collaborativa, fogli di calcolo, mappe mentali), web hosting (tipo Dropbox, iCloud, Google Drive ecc.), social, chat personali, strumenti per programmatori… Per farla breve: pensa ad un servizio online che usi comunemente ed e sappi che ne esiste anche la versione libera e aperta, fatta eccezione giusto per i fornitori di media mainstream coperti da copyright come Spotify o Netflix e iTunes, ecco, ma se pensi a Evernote, Dropbox, Twitter, Facebook, Google Maps, Gmail, Whatsapp, le ricerche su Google, iWork e tutti quegli strumenti che usi quotidianamente online beh, ognuno di questi ha la sua controparte libera!
Alcuni di questi strumenti sono parzialmente sovrapponibili; un esempio é l’applicazione Turtl che é sia un gestore appunti (Notebook) che uno strumento per archiviare link interessanti (Bookmark manager) che fa dunque un pò quello che fa Evernote ed un pò quello che fa Pocket. Questo per dire che in alcuni casi la definizione usata per classificare questi strumenti può essere poco esaustiva.
Altra cosa interessare é che uno stesso provider può mettere a disposizione più strumenti che fanno la stessa cosa (ad esempio due diversi tipi di calendario o di strumenti di scrittura). La cosa può confondere un attimo chi non é abituato a dover scegliere tra opzioni diverse con uno stesso provider, ma va tutta a favore della personalizzazione (ti trovi scomodo ad usare EtherPad? Nessun problema: abbiamo anche PadLand!)
Certi strumenti software sono molto popolari e vengono messi a disposizione da diversi provider (per esempio, chi offre un servizio di data hosting nel 99% dei casi utilizza NextCloud), che però ne personalizzano un pò l’estetica, a volte alcune funzioni e spesso anche il nome (per esempio, il server Nextcloud messo a disposizione da Framapiaf viene chiamato “Framadrive”). Altri invece, sono più rari.
Questo post non é incentrato sulle funzionalità dei singoli strumenti software e qui si vuol solo elencare una serie di provider di strumenti FLOSS che, volendo, un utente potrebbe anche installarsi su un proprio server. Pertanto l’elenco non comprende siti che mettono a disposizione un unico strumento software (tipo mastodon.social che mette a disposizione solamente la propria Istanza Mastodon) e/o strumenti software non hostabili privatamente (tipo DuckDuckgo)

PAESE: Italia
FINANZIAMENTO: Donazioni
A/I é il principale riferimento italiano per quanto riguarda collettivi antagonisti e anticapitalisti impegnati per i diritti digitali. Offre tutta una serie di strumenti con un fortissimo occhio di riguardo a sicurezza e protezione dati.

PAESE: Italia
FINANZIAMENTO: Donazioni e sottoscrizioni

PAESE: Italia
FINANZIAMENTO: Donazioni

PAESE: Francia
FINANZIAMENTO: Parte in donazioni, parte a pagamento
Cryptpad é una compagnia francese che realizza e mette a disposizione una serie di propri strumenti focalizzati su privacy e sicurezza online.

PAESE: Olanda
FINANZIAMENTO: Donazioni
Disroot é un’organizzazione di hacktivisti di impronta libertaria impegnata a far conoscere le tecnologie aperte ed a diffondere una maggior cultura della privacy informatica.

PAESE:
FINANZIAMENTO: Il progetto é finanziato direttamente dai suoi membri attivi
FeNeAs é un’associazione no profit il cui scopo é diffondere l’utilizzo di strumenti digitali federati

PAESE: Francia
FINANZIAMENTO: Donazioni
Framasoft é un’importante associazione francese il cui scopo é quello di diffondere l’uso di tecnologia FLOSS. Framasoft organizza incontri, corsi ed un gran numero di attività diverse. In particolare sta portando avanti il progetto di de-googleizzare il web, facendo conoscere tutti gli strumenti già esistenti ed utilizzabili anche senza dover per forza rivolgersi alle big company dell’informatica. Gli strumenti che offre Framasoft sono davvero tantissimi e non sarà possibile elencarli tutti, ma ci si prova. Una caratteristica particolare é che Framasoft ribattezza gran parte degli strumenti offerti “Frama(qualcosa)”. Il sito é in francese ma gran parte é tradotto in inglese e sempre più pagine sono tradotte anche in italiano.

PAESE: USA
FINANZIAMENTO: Servizi a pagamento
Librem é il marchio dei prodotti e servizi open dell’azienda Purism. Purism produce computer desktop e smartphone di alta fascia che promettono una alta attenzione al rispetto della privacy e della sicurezza informatica. I servizi della linea Librem derivano da strumenti FLOSS che però vengono fortemente personalizzati e rinominati “Librem(qualcosa)”; per esempio, il server Mastodon offerto da Framasoft si chiama FramaPiaf.

PAESE: ?
FINANZIAMENTO: Donazioni
Nixnet é creato e gestito apparentemente da una sola persona, Amolith, che mette a disposizione gli stessi strumenti che lui utilizza. Molto servizi sono utilizzabili anche attraverso TOR e c’é forte attenzione su sicurezza e criptatura dei messaggi.

PAESE: Lussemburgo
FINANZIAMENTO: Autofinanziamento

PAESE: USA
FINANZIAMENTO: Donazioni
RiseUp é un collettivo di Seattle ma con membri sparsi in tutto il mondo. É attivo dal 1999 e si adopera per una società libera ed una lete altrettanto libera.

PAESE: Germania
FINANZIAMENTO: ?

PAESE: Italia
FINANZIAMENTO: ?
A cura dell’associazione Bije di Verona, che si occupa di diffondere l’utilizzo di strumenti FLOSS
Grazie ad https://mastodon.bida.im/@hannahliu e https://ins.mastalab.app/@metalbiker per lo scambio su Mastodon da cui é nata l’idea per questo articolo.