❌

Vista elenco

Enrico De Pedis: l'arresto che spaccò la Banda della Magliana

28 Settembre 2026 ore 22:14

💾

Dopo la morte di Danilo Abbruciati, gli equilibri della Banda della Magliana cambiano rapidamente. Enrico De Pedis, già figura centrale del gruppo dei Testaccini, attraversa una delle fasi più delicate della sua storia criminale, mentre all'interno della Banda aumentano tensioni, rivalità e nuovi rapporti di forza.

In questo documentario ricostruiamo il periodo che va dalla morte di Abbruciati all'arresto di Enrico De Pedis nel 1984: gli uomini che lo circondano, i contrasti all'interno della Banda della Magliana e gli avvenimenti che conducono alla sua cattura.

━━━━━━━━━━━━━━━━━━━━━━

📌 IN QUESTO DOCUMENTARIO SCOPRIRAI

✔ Cosa cambia nella Banda della Magliana dopo la morte di Danilo Abbruciati
✔ Il ruolo di Enrico De Pedis e del gruppo dei Testaccini
✔ Le tensioni e i nuovi equilibri all'interno della Banda
✔ I rapporti tra i diversi gruppi della criminalità romana
✔ Gli avvenimenti che precedono l'arresto di De Pedis
✔ L'arresto di Enrico De Pedis nel 1984

━━━━━━━━━━━━━━━━━━━━━━

📺 QUESTA INCHIESTA FA PARTE DELLA SERIE

Banda della Magliana

▶️ Guarda gli altri documentari della serie nella playlist dedicata sul canale Italia Mistero.

━━━━━━━━━━━━━━━━━━━━━━

▶️ ISCRIVITI A ITALIA MISTERO
https://www.youtube.com/@italiamistero

🔐 ABBONATI AL CANALE
Accedi all'Archivio Italia Mistero e ai contenuti riservati:
https://www.youtube.com/@italiamistero/join

🌐 ARCHIVIO E APPROFONDIMENTI
https://www.italiamistero.it

━━━━━━━━━━━━━━━━━━━━━━

⚠️ AVVERTENZA

Questo video è frutto di ricerca giornalistica e utilizza solo fonti pubbliche e accessibili.
Alcune immagini o brevi spezzoni video sono riprodotti per finalità di cronaca, critica, commento o informazione ai sensi dell'art. 70 LDA.
Le ricostruzioni hanno esclusivamente scopo divulgativo.
Non vengono promossi comportamenti contrari alla legge.
Questo contenuto NON costituisce pubblicità né contiene contenuti sponsorizzati.

NASA Armstrong Celebrates 80 Years of Flight Innovation

28 Settembre 2026 ore 21:20

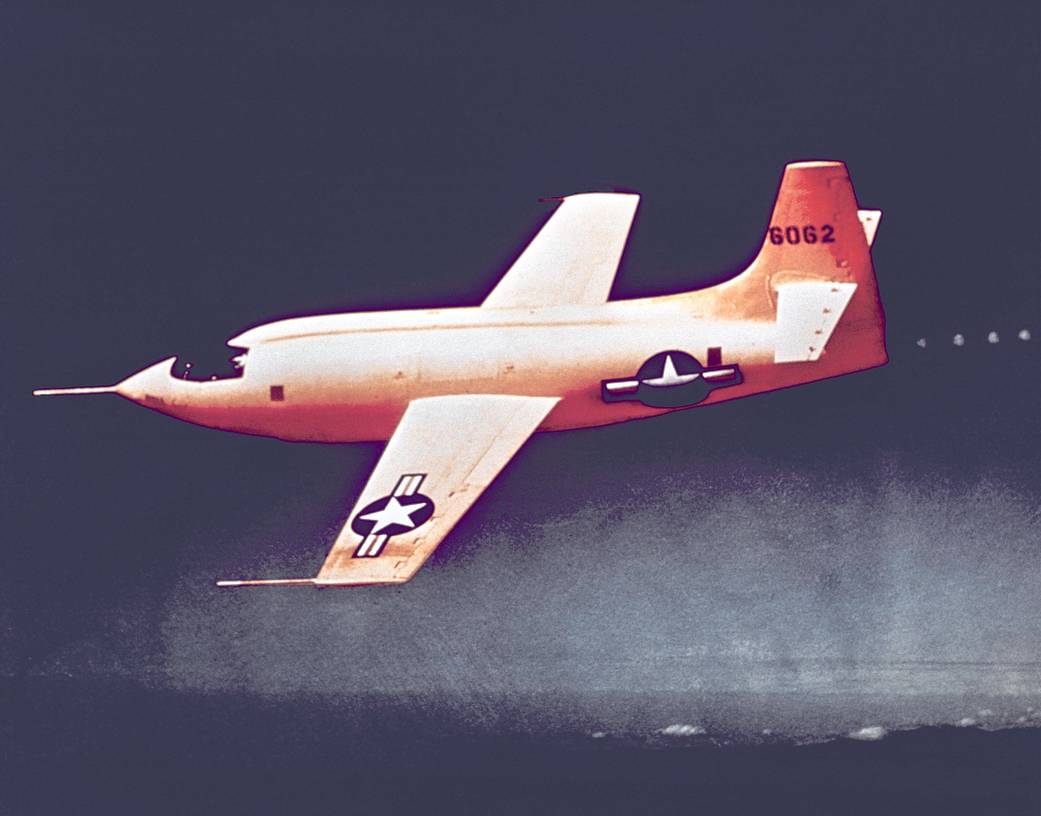
On Sept. 30, 1946, five National Advisory Committee of Aeronautics (NACA) engineers arrived at Muroc Army Airfield in California’s high desert to achieve supersonic flight for the first time. In less than two years, NACA flew the X-1 aircraft faster than the speed of sound, marking an important milestone in aviation history.

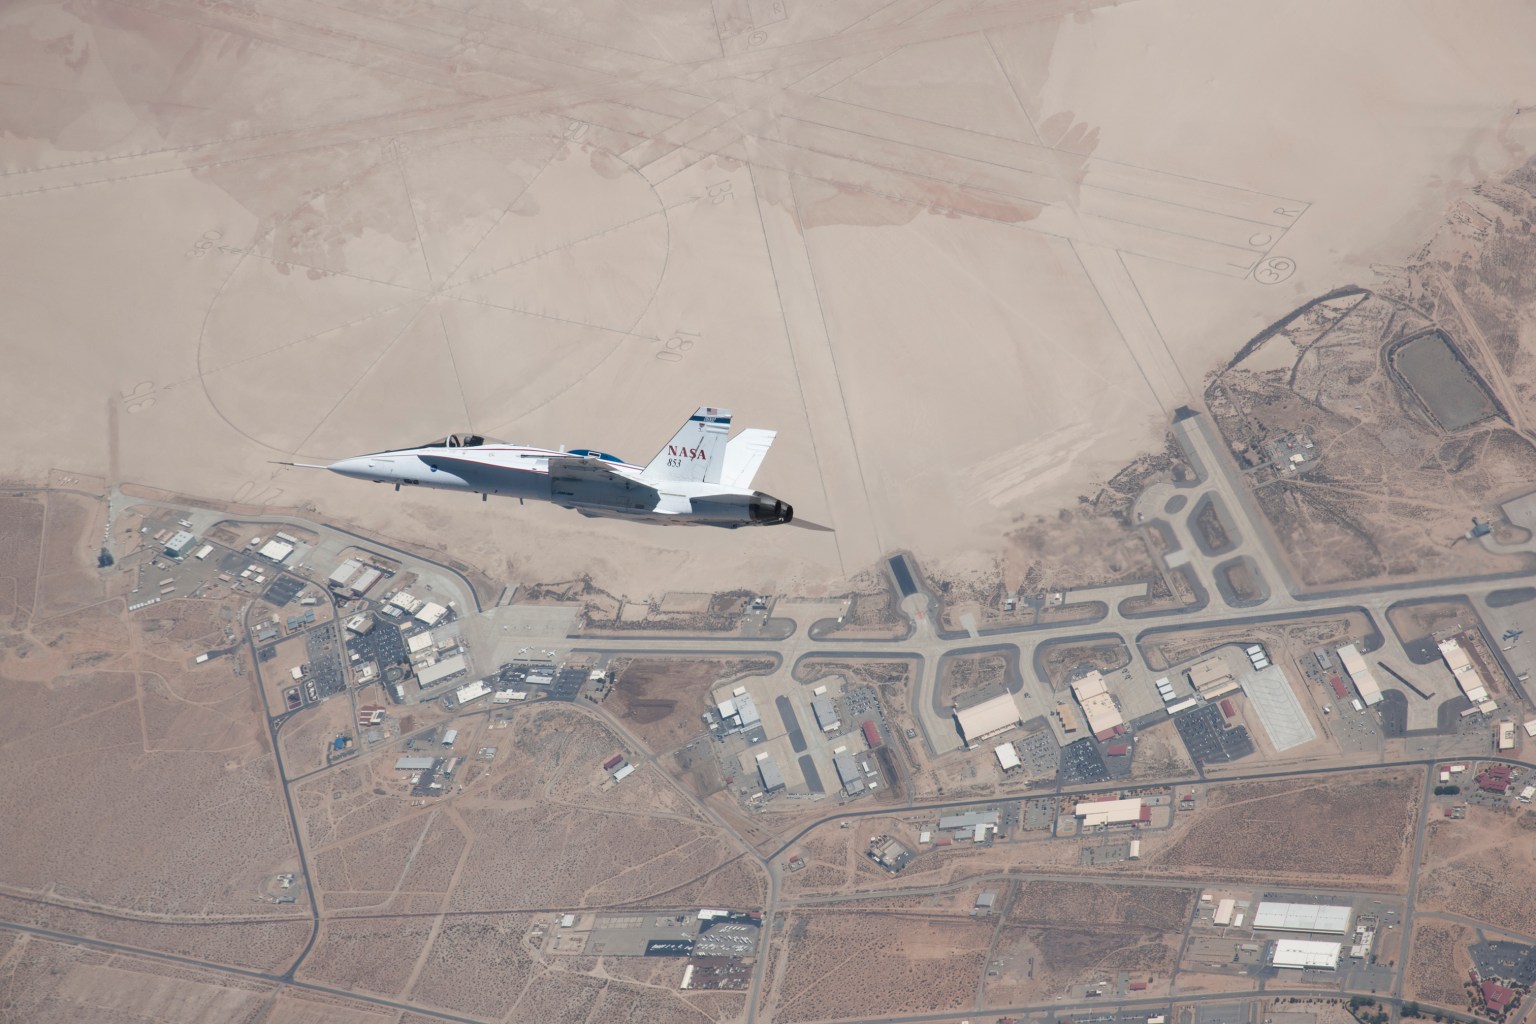
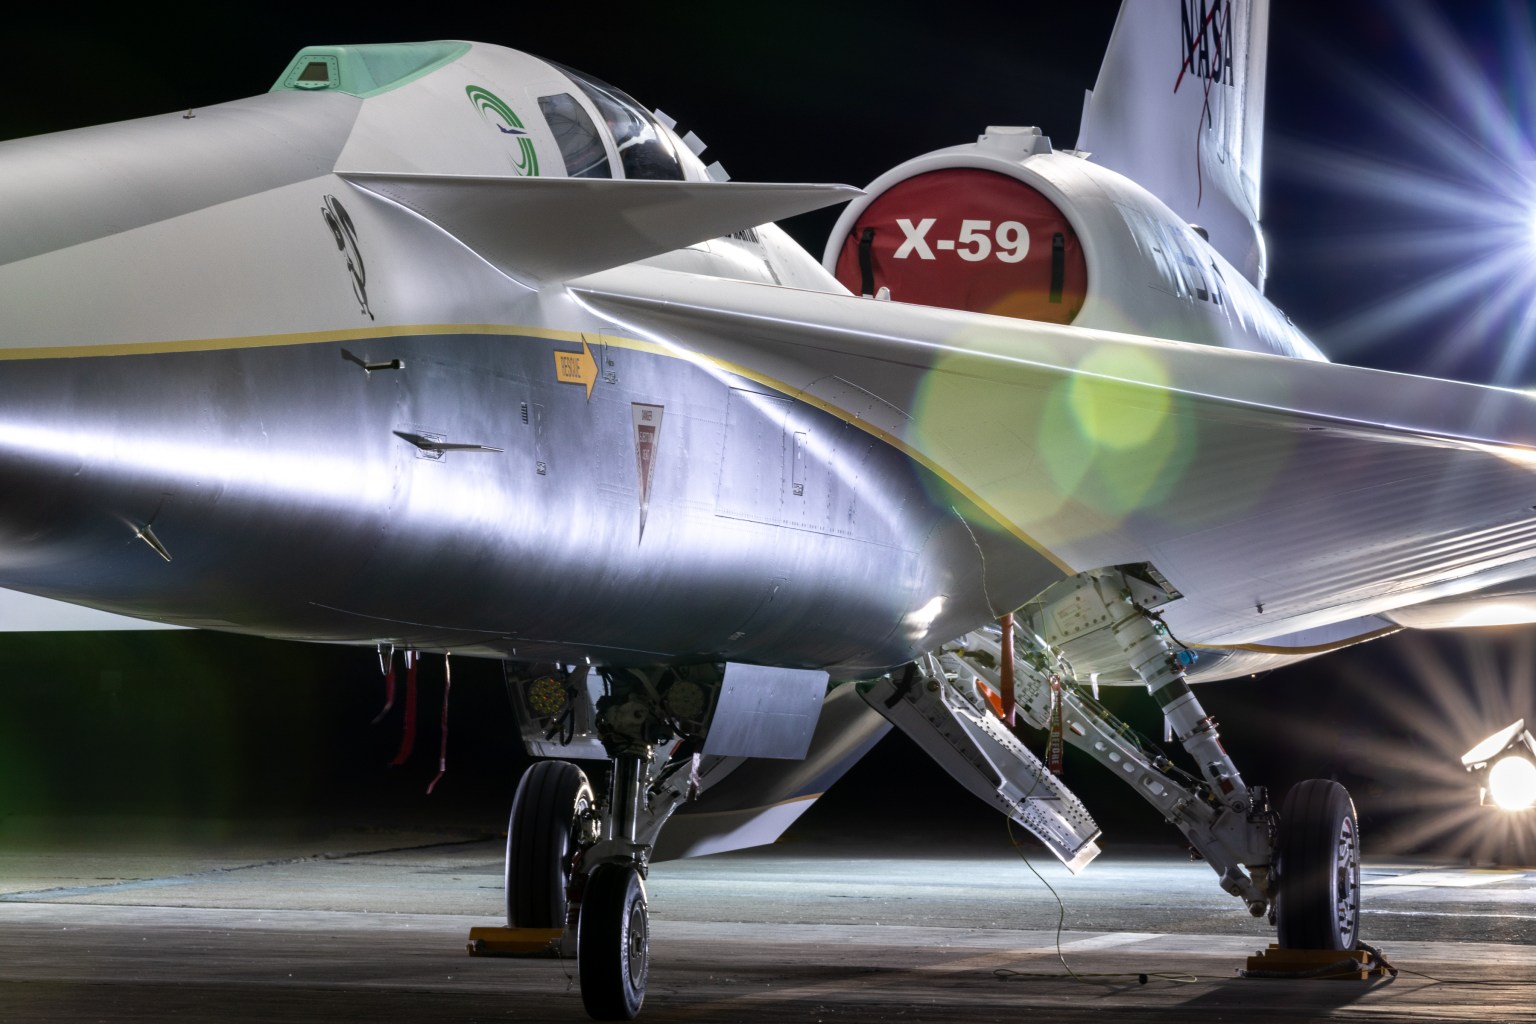
Fast forward 80 years, and that former NACA outpost is now NASA’s Armstrong Flight Research Center in Edwards, California, flying the X-59 supersonic X-plane in the same skies to demonstrate that supersonic flight doesn’t have to come with a boom.

Over Armstrong’s 80-year history, the center has supported milestone missions ranging from space shuttle landings to SR-71 flights, shaping the evolution of science, aeronautics, and space research.

This Southern California NASA center is poised to lead the next era of aeronautics and human spaceflight, advancing technologies that will define the future of flight.

Fast facts

  • NASA Administrator Jared Isaacman recently named Armstrong as the agency’s Center of Excellence for Flight Test and Aircraft Operations, recognizing the center’s unmatched rigor in executing unique missions only NASA can fly.
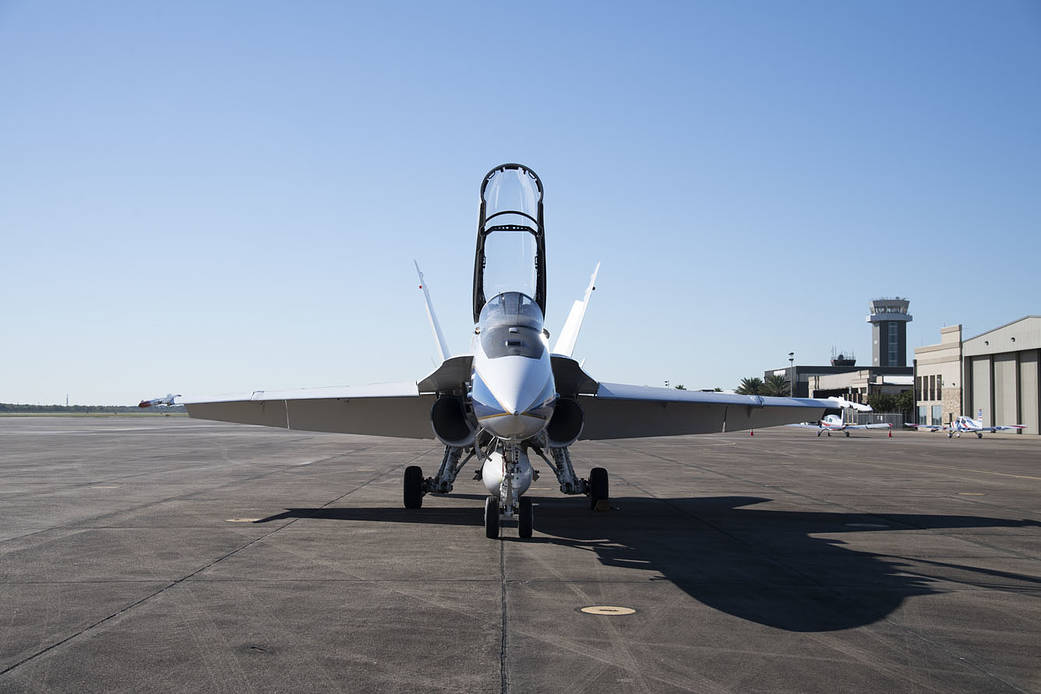
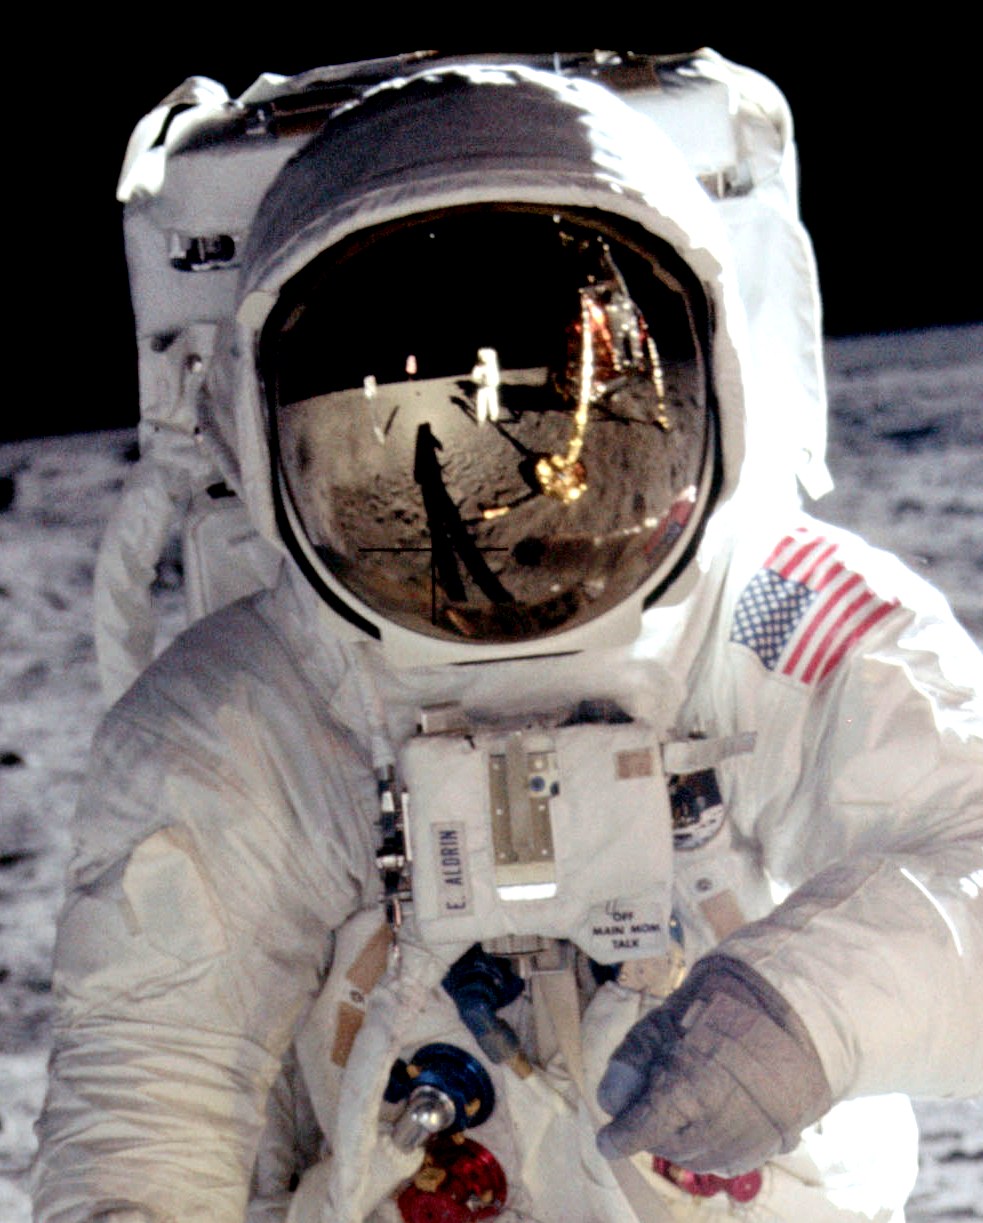
  • To support NASA’s Artemis missions and return to the Moon, Armstrong uses research aircraft such as a 737 for astronaut suit testing, the G-III for Artemis II heat-shield data collection, and an F/A-18 aircraft that tested the autopilot for the SLS (Space Launch System) rocket.
  • NASA’s aeronautics centerpiece, the X-59, is undergoing rigorous testing and a series of flights at Armstrong to prepare for upcoming quiet supersonic demonstrations over U.S. communities.
  • NASA Armstrong has transformed commercial and military aviation — from early supersonic flight research to digital fly-by-wire — and continues working with other government agencies, industry, and academia to make flying safer, more autonomous, and more efficient.
  • The center plays a vital role in global science by flying aircraft like the ER-2, C-20A, and Gulfstream G-III/IV/V to collect critical data on wildfires, glacier melt, pollution, minerals, and more.

Behind these achievements are the engineers, pilots, technicians, and mission support teams who continue to push the boundaries of what’s possible.

For more about NASA Armstrong, visit:

https://www.nasa.gov/armstrong

-end-

Dede Dinius / Teresa Whiting
Armstrong Flight Research Center, Edwards, California
661-276-3449
darin.l.dinius@nasa.gov / teresa.whiting@nasa.gov

💾

Red, White, and Boom, the U.S. Air Force Test Center’s celebration of America’s 250th anniversary and NASA Armstrong’s commemoration of its 80th year, was Fr...

E SE IL MONDO NON FOSSE COME LO PENSIAMO? Nietzsche, Nāgārjuna, Wittgenstein

28 Settembre 2026 ore 19:06
Nietzsche, Nāgārjuna e Wittgenstein mettono in discussione il nostro modo abituale di pensare la realtà.Dalla «logicizzazione» del mondo alla vacuità buddhista, fino al limite del linguaggio e al mistico.E se i nostri concetti non fossero la realtà, ma soltanto il modo in cui riusciamo ad abitarla? 🎬 PREMIERE📅 29/09/2026 ore 14.00🔗https://youtu.be/OFzkZjW4Z4k E se il mondo […]

BAD DRIVERS OF ITALY dashcam compilation 9.28 - SIGNORAAA

28 Settembre 2026 ore 18:00

💾

Trova la tua prossima DASHCAM https://sicurisullastrada.it/dashcam/
Dubbi o domande? Trovi qui le RISPOSTE https://sicurisullastrada.it/dashcam-5-minuti-per-sapere-tutto/
Vuoi inviarci le clip della TUA DASHCAM? Guarda come fare su https://bit.ly/inviavideo
Seguici sui canali BDOI per essere AGGIORNATO e vedere le MIGLIORI CLIP https://bit.ly/canalibdoi
Hai domande o curiosità? COMMENTA sotto al video oppure CONTATTACI https://bit.ly/contattabdoi
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
This video shows DANGEROUS behaviors not to imitate! Always drive carefully!
Do you want to send us the clips of YOUR DASHCAM? See how on https://bit.ly/inviavideo
Follow us on BDOI channels to be UPDATED and see the BEST CLIPS https://bit.ly/canalibdoi
Do you have any questions or curiosities? COMMENT below the video or CONTACT US https://bit.ly/contattabdoi

#baddriversofitaly #dashcam #compilation

Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation

28 Settembre 2026 ore 17:08

Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p.

According to three sources familiar with the matter, the Dutch man arrested by authorities this month is Pepijn van der Stap, a convicted cybercriminal from Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in 2023 in connection with a string of data thefts and extortions that prosecutors said earned between €1.5 million and €2.7 million.

At his trial in late 2023, van der Stap admitted that he lived a Dr. Jekyll and Mr. Hyde existence, secretly using the hacker handle “Umbreon” to extort victims and post their data on English language hacking communities like the now-defunct RaidForums and Breached. By day, however, van der Stap was working as a software engineer at the Amsterdam-based cybersecurity startup Hadrian, while volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research group.

Pepijn van der Stap’s alter ego “Umbreon” selling a database on RaidForums, offering information on 2.3 million people from The Netherlands in September 2021. This user’s avatar is a depiction of the Pokemon character Umbreon. Image: KELA.

Van der Stap confessed to his data theft and extortion activity, and was sentenced to four years in prison (one of which was suspended). During his trial, van der Stap opted to remain in custody for a time rather than at home, saying he could not find better treatment on the outside for his ongoing psychological issues, which he claimed included PTSD related to childhood trauma. He was released from prison in December 2025.

In an interview with KrebsOnSecurity on September 9, 2026, Van der Stap cast himself as a reformed hacker who was trying to turn his life around and make a positive contribution to society. Van der Stap is currently employed as offensive security lead at the Dutch company Neo Security, which did not respond to requests for comment.

Van der Stap said he was still dealing with civil lawsuits and restitution related to his previous cybercrime victims, and that he was trying his best to make amends. But not long after that interview, the Dutch hacker abruptly stopped replying to messages. Efforts by others close to him also repeatedly failed to elicit a response for the past two weeks.

The LinkedIn profile for Pepijn van der Stap.

According to two sources with knowledge of the matter, Van der Stap was arrested by Dutch authorities on or around September 16, and has been held in custody for questioning since. One source said a colleague of theirs personally witnessed Dutch authorities carting items out of Van der Stap’s residence.

Authorities in the Netherlands have been asking the public for help in identifying the voice in a recorded telephone call from February 2026 in which a native Dutch-speaking ShinyHunters member social engineered their way into Odido, the nation’s largest mobile telecommunications provider. In that intrusion, ShinyHunters tricked an Odido employee into logging in at a spoofed website, and then used that access to steal data on more than 6.2 million Dutch people.

Responding to Dutch news media, ShinyHunters confirmed that the suspect in the audio clip is indeed a member of the hacker collective.

“Our team member has our full support – emotionally, mentally, and financially,” the hackers said. “Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them,” reads a statement ShinyHunters shared with NL Times. It remains unclear if the Dutch police have matched the Odido caller to a confirmed real-life identity. The Dutch police unit handling the Odido incident did not respond to requests for comment.

The group also lashed out at the authorities in the Netherlands. “The Dutch police will need all the luck in the world – and everyone’s prayers – if they want to catch him before we carry out another large-scale data theft in the Netherlands,” the ShinyHunters statement said. “Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless.”

FBI, CL0P HACKS

Just days after sources say Van der Stap was detained by Dutch authorities, ShinyHunters claimed credit for an unusually brazen breach at the FBI’s job application site apply.fbijobs.gov. According to reporting from 404 Media, the data stolen from the FBI site includes Social Security numbers and personal information on more than 5,000 officials.

404 Media and Reuters reported the FBI data included each person’s job title or team, such as special agent, threat intake examiner, major cybercrimes unit, and those investigating cyber threats from foreign state-backed actors. Reuters examined documents shared by ShinyHunters and found they included sensitive psychiatric and medical files of FBI staff. The FBI issued a brief statement confirming the hack.

ShinyHunters said it gained access to the FBI site and other victims by exploiting a recently patched vulnerability (CVE-2026-35273) in PeopleSoft, a software-as-a-service platform from the software giant Oracle that is broadly used by companies to manage hiring and human resources, benefits and payroll. Oracle quickly issued a fix for the Peoplesoft vulnerability that ShinyHunters reportedly began exploiting as a zero-day in June, and at the time Mandiant released web application firewall rules intended for organizations who couldn’t apply the security update quickly enough.

But on Friday, BleepingComputer reported that ShinyHunters used a URL-encoding trick to bypass Mandiant’s suggested web application firewall rules designed to mitigate the threat from the PeopleSoft flaw. In a report released Sept. 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability to steal data from dozens of systems across a range of industries, including higher education, technology, healthcare, agriculture, transportation and government.

Van der Stap’s former hacker alias Umbreon was hidden in plain sight throughout the imagery ShinyHunters used to spread news about the FBI hack: The defacement image that ShinyHunters left behind on the hacked FBI jobs site included an ASCII art design featuring the Pokemon character Umbreon. The message at the top read, “This site has been seized by ShinyHunters. rooting your systems since ’19 ;)” The image appears identical to a defacement message ShinyHunters used in their 2020 hack of the English-language cybercrime community Hackforums.

The defacement message left by ShinyHunters on the FBI jobs site included an ASCII art rendition of the Pokemon character Umbreon. Image: Bleeping Computer.

Multiple sources close to the ShinyHunters investigation said the group’s recent risky attacks against the FBI and one of Russia’s most venerated ransomware groups amounted to a major pivot away from the more measured tenor of the hacking gang’s operations. Those sources said the sudden shift came about after ShinyHunters was taken over by a teenage cybercriminal from Amman, Jordan who goes by the nickname Rey and operates as part of a cybercrime group called ScatteredLapsussHunters (SLSH), which experts say is an amalgamation of three hacking groups — Scattered Spider, LAPSUS$ and ShinyHunters.

Those sources said Rey had an ongoing beef with the Dutch hacker over control of the ShinyHunters brand and data, and that the inclusion of the oversized Umbreon Pokemon image in the FBI jobs site defacement was likely an attempt by Rey to pin the hack on the Dutchman.

Rey was first publicly identified by the cybersecurity firm KELA in March 2025. In advance of our November 2025 profile of Rey, KrebsOnSecurity messaged Rey’s father and asked for permission to interview his teenage son. Rey’s dad merely forwarded the message to his son, who admitted to participating in ransomware attacks and said he was trying to extricate himself from the SLSH hacker group.

BLAMING UMBREON

Immediately after news of the FBI jobs site hack was picked up in the media, Rey’s main account on Twitter/X (Ryan Moran/@rmoskovy) was taunting the Cl0p ransomware group and the FBI, crudely depicting them as the twin towers in New York being struck by planes labeled “cl0p drama” and “fbi breach claim.” In the foreground of the city is the giant Pokemon figure of Umbreon.

A taunting meme uploaded to Twitter/X by Rey’s now-defunct account on Sept. 22. A giant float-sized version of the Pokemon character Umbreon can be seen in the bottom left.

On Sept. 24, KrebsOnSecurity again contacted Rey’s dad, asking to interview him and his son for a story on Rey’s apparent ascendency as the head of ShinyHunters. Just hours after that request, Rey deleted his longtime Twitter/X account. Meanwhile, Rey’s dad, who works for the Royal Jordanian Airlines, has failed to respond to a half-dozen emailed requests for comment about his son’s alleged activities.

Where does the bad blood between SLSH and ShinyHunters come from? According to a story in Wired this month, ShinyHunters and SLSH members briefly partnered earlier this year to help better monetize important stolen credentials collected by TeamPCP, an upstart group that was having great success compromising global code supply chains with malicious software but hadn’t been able to profit much from their stolen data (two alleged leaders of TeamPCP were arrested last month in Australia, and in an interview the TeamPCP leader claimed they made just $20,000).

The Wired story noted how Mandiant had infiltrated TeamPCP and was secretly responsible for having the crime group’s stolen credentials burned so quickly: Mandiant was secretly feeding those credentials to the major cloud providers like Amazon and Microsoft, who quickly invalidated the stolen keys. Meanwhile, the formerly cooperating hacker groups began to blame one another for causing the credentials to become worthless.

Wired’s Andy Greenberg reported that a few weeks after partnering with TeamPCP, “ShinyHunters went rogue, carrying out its own extortions with TeamPCP’s credentials but without giving the supply-chain hackers their cut.”

Mandiant researcher Austin Larsen told KrebsOnSecurity earlier this month that ShinyHunters has been enjoying a successful extortion spree so far this year, and is on track to pull in nearly $100 million in extortion payments from cybercrime victims in 2026.

Van der Stap claims he was never motivated by money and that his earlier hacker activity was driven by a desire to have the world’s most complete collection of stolen databases. Speaking with reporters from Bloomberg in 2024, Van der Stap said that singular focus in turn fueled his desire to carry out cyberattacks.

“The hacking was very easy for me, and it wasn’t a compulsion,” he told Bloomberg. “My habit was collecting. Collecting data, organizing data, downloading data, creating folders.”

DIVD, the nonprofit security research group where Van der Stap previously served as a volunteer, disclosed on LinkedIn last week that the organization was dealing with an internal cybersecurity incident that appears to have involved the malicious use of artificial intelligence. DIVD has released few details about that incident, but a spokesperson for the nonprofit told KrebsOnSecurity it does not appear related to ShinyHunters, nor are there any signs the matter involves the work of a previous volunteer.

Update: 3:44 p.m. ET: Corrected Van der Stap’s age, which is 24 (not 23).

Update, 4:54 p.m. ET: The Dutch police have confirmed the arrest of a 24-year-old in connection with the ShinyHunters investigation. In a statement on Twitter/X, the Dutch police said the man will appear on Tuesday, September 29 before the chambers of the Rotterdam District Court, and that it will provide more information tomorrow.

Sept. 29, 9:42 a.m. ET: The Dutch news outlet RTL reports that investigators suspect Van der Stap tried to orchestrate at least two murders. RTL reported the two murders were allegedly to be committed abroad, and that there are indications the suspect gave the order for this.

The FBI released a short video message on the ShinyHunters investigation from Brett Leatherman, assistant director of the FBI’s cyber division, who thanked Dutch law enforcement partners for their assistance and urged remaining ShinyHunters members to turn themselves in.

“Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left,” Leatherman said. “The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours.”

Xi Jinping demands ‘safer’ China as Communist Party prepares for leadership reshuffle

President Xi Jinping has ordered China’s security and legal apparatus to relentlessly eliminate risks and build a “safer” country a year ahead of the pivotal 21st Communist Party congress, which will usher in a major leadership reshuffle. The latest instruction, published by state news agency Xinhua on Monday night, is also the Chinese leader’s first major domestic directive since his state visit to Washington last week, signalling a pivot back to the domestic agenda – especially stability. In a...

Practicing for Safe Landings on the Moon and Beyond

24 Settembre 2026 ore 18:29
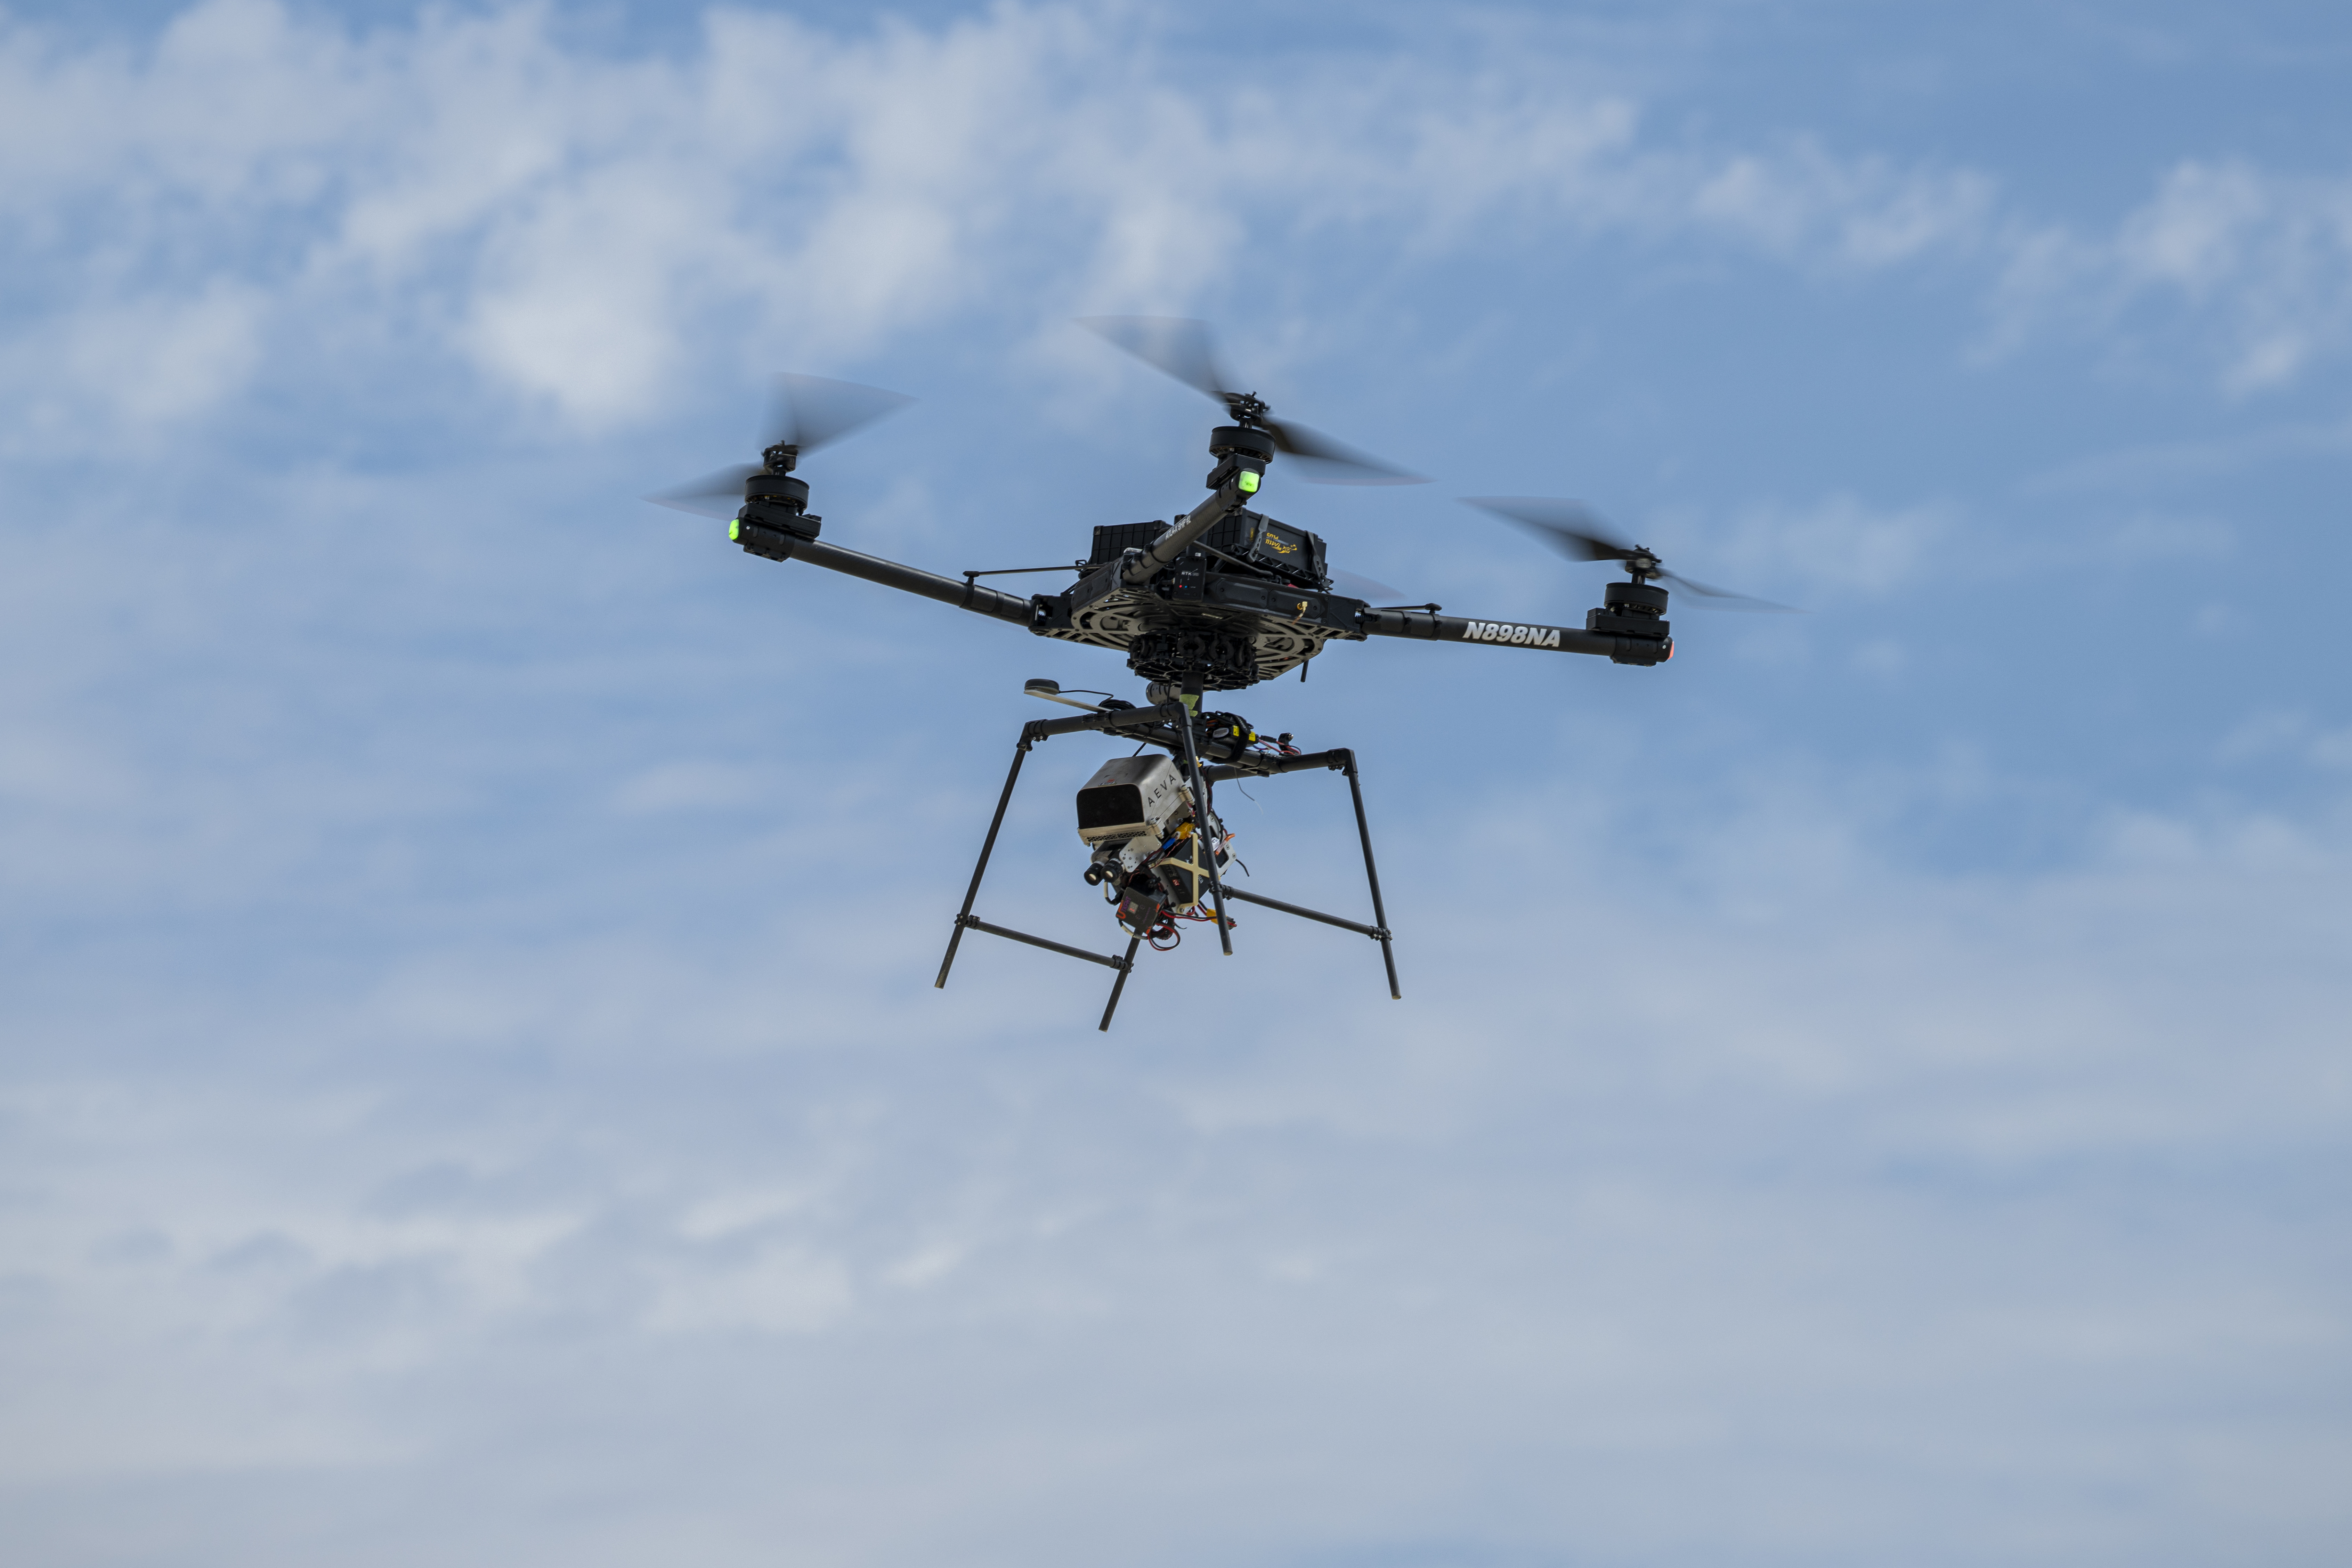
A remotely piloted drone with four rotors carries a guidance and navigation experiment through flight maneuvers.
NASA/Ryan Kline

In this Aug. 27, 2026, image, an Alta-X drone flies an advanced guidance and navigation system known as the Safe and Precise Landing – Integrated Capabilities Evolution (SPLICE) experiment near NASA’s Armstrong Flight Research Center in Edwards, California.

Researchers at NASA’s Johnson Space Center in Houston developed SPLICE, which successfully completed simulated lunar descent and landing maneuvers during recent testing. Its technologies provide safe and precise landing for the Moon, Mars, icy worlds, and other destinations using specialized navigation, guidance, and processing techniques. It enables landing in hard-to-reach and unknown areas that are of high scientific interest.

Image credit: NASA/Ryan Kline

SAN LORENZO FUORI CONTROLLO: Cosa Succede Davvero di Notte a Roma

28 Settembre 2026 ore 13:00

💾

Roma, San Lorenzo. Uno storico quartiere popolare che nel corso degli anni ha ceduto il passo alla movida incontrollata, al fuorisede e al turismo mordi e fuggi.

A pochi passi dalla stazione Termini, la quotidianità dei residenti fa ormai i conti con degrado, microcriminalità e insicurezza: continue notizie di aggressioni, rapine e soggetti pericolosi che presidiano le strade a qualsiasi ora, di fronte a interventi istituzionali spesso considerati insufficienti da chi vive qui. Chi può, getta la spugna, vende casa e va altrove.

Siamo stati a San Lorenzo durante il fine settimana per documentare la reale situazione sul campo e capire quanto sia diventato rischioso vivere in questa zona, soprattutto per le persone più fragili.

💬 Diteci la vostra nei commenti: avete mai vissuto situazioni simili a San Lorenzo o in quartieri analoghi nella vostra città?

📌 Iscriviti al canale e attiva la campanella per non perderti i prossimi reportage.

#Roma #SanLorenzo #Reportage #Sicurezza #DegradoUrbano

La legalizzazione sperimentale in Svizzera cambia il modo di consumare, non le quantità

28 Settembre 2026 ore 12:39
Si entra, si sceglie tra fiori, resina o una ricarica per vaporizzatore, si ascolta qualche consiglio dal farmacista e si esce. Succede dal 2024 in nove farmacie della Svizzera – cinque a Berna, tre a Lucerna, una a Bienne – dove 1.177 consumatori abituali acquistano cannabis legalmente nell’ambito dello studio SCRIPT, condotto dalle università di …

ROMI Company porta l’intelligenza artificiale nei processi aziendali

28 Settembre 2026 ore 11:44
Team aziendale al lavoro su dati e processi con strumenti digitali
L’intelligenza artificiale crea valore quando entra nei processi aziendali con obiettivi, dati, KPI e responsabilità chiare. Dalle attività ripetitive alle decisioni supportate dai dati, ecco come trasformare l’AI da semplice strumento a leva operativa.

L'articolo ROMI Company porta l’intelligenza artificiale nei processi aziendali proviene da FullPress.

LESSICO PER LA REPUBBLICA. Corso di formazione e incontro pubblico: ciclo “La Repubblica dei partiti”

28 Settembre 2026 ore 10:59

LESSICO PER LA REPUBBLICA. Corso di formazione e incontro pubblico: ciclo “La Repubblica dei partiti”

Venerdì 9 ottobre 2026 alle 17.00, a Palazzo dell’Orologio (sede ISTORECO, Piazza Luigi Orlando), prende avvio “La Repubblica dei partiti: ideologie, famiglie politiche e pratiche nella democrazia italiana”. È un corso di formazione e ciclo di incontri pubblici che ripercorre la storia dell’Italia repubblicana attraverso i partiti. Nei primi decenni della Repubblica furono loro a organizzare la partecipazione, formare le classi dirigenti e dare forma alle culture politiche del Paese.

Il ciclo si apre con Lessico per la Repubblica. Dal Risorgimento all’integrazione europea (il Mulino), diretto da Maurizio Ridolfi. Un’opera collettiva di oltre cento studiosi che ricostruisce le parole chiave del linguaggio repubblicano: come sono nate, come hanno cambiato significato, come hanno accompagnato la storia italiana dall’Unità all’Europa.

Il libro è anche uno strumento di educazione civica, utile per capire le radici della democrazia di cui i partiti sono stati protagonisti.

Ne discutono con l’autore Marco Manfredi (Università di Pisa), Angelo Gaudio (Università di Udine) ed Enrico Mannari (già Luiss School of Government). Coordina Federico Creatini (Università della Calabria).

La partecipazione è libera e gratuita.

Per i docenti il corso è su piattaforma SOFIA, codice 106752.

Premio Simonetta Ortaggi per tesi di storia del lavoro (scadenza 31 dicembre 2026)

28 Settembre 2026 ore 10:38

Premio Simonetta Ortaggi per tesi di storia del lavoro (scadenza 31 dicembre 2026)

Pubblichiamo il bando della quinta edizione del premio “Simonetta Ortaggi” – promosso dalla SISLav e dall’Istoreco di Livorno – e rivolto alle tesi di dottorato discusse negli ultimi tre anni.

Scarica il pdf del bando

Per sostenere lo sviluppo di nuove ricerche sui temi della storia del lavoro, la Società Italiana di Storia del Lavoro (SISLav) e l’Istituto Storico della Resistenza e della Società Contemporanea nella provincia di Livorno (Istoreco Livorno) hanno istituito nel 2016 un premio intitolato alla storica Simonetta Ortaggi, scomparsa nel 1999, studiosa e autrice di alcuni tra i più importanti e sistematici studi italiani di storia del lavoro. La quintaedizione del premio è riservata a tesi di dottorato sulla storia del lavoro discusse neltriennio 2024-2026. Possono concorrere tesi discusse presso una Scuola di dottorato italiana, senza vincoli relativi al periodo storico o all’area geografica oggetto della ricerca, e tesi discusse presso una Scuola di dottorato straniera, purché dedicate alla storia del lavor in Italia, senza vincoli relativi al periodo storico considerato.

Il Premio consiste nella pubblicazione dell’opera nella collana “Lavori in corso” delle edizioni SISLav-NDF. Il volume sarà pubblicato in open access, con accesso gratuito allaversione elettronica sul sito dell’editore, e sarà inoltre disponibile per l’acquisto in formatocartaceo. In alternativa alla pubblicazione, la vincitrice o il vincitore potrà optare per unpremio in denaro di 1.500 euro.

La tesi di dottorato potrà essere presentata in lingua italiana, francese, inglese, portoghese, spagnola o tedesca.

Condizione necessaria per la partecipazione è che l’opera non sia stata pubblicata né sia incorso di pubblicazione presso un editore. Il deposito della tesi in un archivio istituzionale o in un repository universitario non è considerato, ai fini del presente bando, una pubblicazione editoriale.

La candidatura dovrà essere presentata entro il 31 dicembre 2026, compilando il facsimile allegato e inviandolo all’indirizzo e-mail storialavoro@gmail.com, insieme a una copia digitale della tesi, un abstract in italiano di massimo 4.000 caratteri, un breve curriculumvitae utile a contestualizzare la ricerca nell’ambito del percorso scientifico della candidata o del candidato e l’elenco delle eventuali ulteriori pubblicazioni.

Le opere saranno valutate da un’apposita Commissione, composta da cinque membri, di cui tre nominati dal Direttivo SISLav e due da Istoreco Livorno. Il giudizio della Commissione è insindacabile.

La composizione della Commissione sarà comunicata sul sito della SISLav (www.storialavoro.it) entro il 15 gennaio 2027.

La Commissione comunicherà il nome della vincitrice o del vincitore e l’esito della selezione a tutte le candidate e a tutti i candidati entro il 30 giugno 2027. Qualora nessuna delle opere concorrenti sia ritenuta adeguata sotto il profilo scientifico e/o pertinente rispetto alle finalità del Premio, la Commissione potrà decidere di non assegnarlo. La Commissione potrà inoltre attribuire una o più menzioni speciali a opere non vincitrici ritenute di particolare valore scientifico e raccomandarne la pubblicazione in open accessnella collana “Lavori in corso” delle edizioni SISLav-NDF.

L’assegnazione del premi avverrà in occasione del Festival di Storia del Lavoro, durante il quale la vincitrice o il vincitore presenterà pubblicamente il proprio lavoro di tesi.

Qualora la vincitrice o il vincitore scelga la pubblicazione dell’opera, dovrà inviare all’indirizzo e-mail storialavoro@gmail.com, entro il 1° ottobre 2027, una versione rivista della tesi:

– che tenga conto delle indicazioni scientifiche ed editoriali formulate dalla Commissione;

– conforme alle norme editoriali della collana “Lavori in corso” delle edizioni SISLav-NDF;

– in lingua italiana e, qualora necessario, tradotta a cura e a spese dell’autrice o dell’autore.

Nel lavoro di revisione, la vincitrice o il vincitore potrà avvalersi del confronto con due interlocutori indicati dal Direttivo SISLav.

Il volume sarà pubblicato in open access in formato elettronico sul sito dell’editore e sarà inoltre disponibile in formato cartaceo. All’autrice o all’autore non saranno corrisposti diritti sulle vendite; riceverà gratuitamente 20 copie cartacee del volume.

Puglia Software Open Source - Tecnoestate – nona edizione

25 Settembre 2026 ore 20:23

L’attività è rivolta a ragazze e ragazzi dai 10 anni in su che vogliano affacciarsi al mondo della robotica e domotica amatoriale attraverso la programmazione di Arduino. Sono previsti 2 corsi con incontri settimanali (martedì o mercoledì), dalle 17 alle 19:

MARTEDI’
23, 30 GIUGNO
7, 14, 21, 28 LUGLIO
4, 25 AGOSTO
1, 8, 15 SETTEMBRE

MERCOLEDI’
...

Puglia Software Open Source - Arduino Day 2026 innovazione, formazione e cultura open source a Barletta

25 Settembre 2026 ore 20:21

ARDUINO DAY 2026
innovazione, formazione e cultura open source a Barletta
La Puglia Software Open Source – APS, associazione di promozione sociale attiva sul territorio dal 2012 e riorganizzata nel 2019 come Ente del Terzo Settore, annuncia la propria partecipazione all’Arduino Day 2026, l’evento mondiale dedicato alla creatività elettronica e alla cultura dell’open hardware....

❌